CEH v13 certification is EC-Council’s current AI-powered Certified Ethical Hacker program, designed to validate knowledge of ethical hacking, reconnaissance, system attacks, network security, web application testing, cloud, IoT/OT, wireless security, and cryptography. The core CEH knowledge exam contains 125 multiple-choice questions and lasts four hours. Candidates can also take the optional six-hour CEH Practical with 20 challenges; passing both earns CEH Master. CEH v13 adds AI-driven techniques across the ethical-hacking lifecycle and extensive hands-on cyber-range practice for real-world skill development.

What Is CEH v13 Certification?

The CEH v13 certification, officially delivered by EC-Council, is the 13th version of the Certified Ethical Hacker program. EC-Council now markets the program as CEH AI, reflecting the integration of artificial intelligence into ethical-hacking training. As of August 2026, EC-Council states that CEH is currently on Version 13.The CEH v13 course combines attack methodology, defensive countermeasures, vulnerability analysis, web and network security, cloud, mobile, IoT/OT, and cryptography. Official training includes 20 modules, 221 hands-on labs, 550 attack techniques, and more than 4,000 hacking and security tools.For any CEH v13 study guide or CEH v13 study material, prioritize concepts and attack/defense relationships rather than memorizing commands.

CEH v13 vs v12: What Changed?

The biggest difference in CEH v13 vs v12 is AI-driven ethical hacking throughout the workflow. EC-Council introduced v13 in September 2024 and applies AI concepts across reconnaissance, scanning, gaining access, maintaining access, and covering tracks.

AreaCEH v12CEH v13 / CEH AI
Core ethical hackingStrong focusRetained and updated
AI integrationLimited/not centralEmbedded across hacking phases
Learning approachTheory + labsLearn, Certify, Engage, Compete
Current statusPrevious versionCurrent Version 13
Career preparationOffensive-security foundationAdds AI-assisted workflows and AI-security exposure

For candidates comparing CEH v12 vs v13, v13 is the relevant study target because EC-Council’s current program is Version 13/CEH AI.

CEH v13 Exam: Format, Duration and Passing Score

The CEH v13 exam is knowledge-based. Passing it earns CEH; the practical exam is optional and used to progress to CEH Master.

Exam DetailCEH Knowledge Exam
Exam code312-50
Questions125 multiple-choice questions
Duration4 hours
DeliveryECC Exam / Pearson VUE
Passing scoreVariable cut score, typically 65%–85%
Practical required for CEH?No

EC-Council explains that different exam forms have different cumulative cut scores, so there is no single universal CEH v13 passing score. Its current CEH page says typical cut scores range from 65% to 85%.

CEH v13 Exam Blueprint: What Should You Prioritize?

The official CEH exam blueprint v5.0 groups the exam into nine domains. The published question counts add to 125. The displayed percentages are rounded and total 101%, so use the question counts—not percentage arithmetic alone—when planning study time.

CEH v13 Blueprint DomainQuestionsWeight
Information Security & Ethical Hacking Overview76%
Reconnaissance Techniques2117%
System Hacking Phases & Attack Techniques1915%
Network & Perimeter Hacking3024%
Web Application Hacking1814%
Wireless Network Hacking65%
Mobile Platform, IoT & OT Hacking1210%
Cloud Computing65%
Cryptography65%

The exam-weighting lesson is clear: network/perimeter hacking, reconnaissance, system hacking, and web application hacking dominate the blueprint. Together, these areas account for most of the scored questions.

CEH v13 Syllabus and Modules

The official CEH v13 syllabus contains 20 modules. Rather than treating the CEH modules v13 as isolated chapters, group them by attack lifecycle:

  • Discovery: Introduction to Ethical Hacking, Footprinting and Reconnaissance, Scanning Networks, Enumeration.
  • Assessment and exploitation: Vulnerability Analysis, System Hacking, Malware Threats.
  • Network attacks: Sniffing, Social Engineering, Denial-of-Service, Session Hijacking, Evading IDS/Firewalls/Honeypots.
  • Application attacks: Hacking Web Servers, Hacking Web Applications, SQL Injection.
  • Modern environments: Wireless Networks, Mobile Platforms, IoT/OT, Cloud Computing.
  • Protection and trust: Cryptography.

The CEH v13 objectives also include AI-supported exercises in areas such as footprinting, scanning, enumeration, vulnerability analysis, system hacking, social engineering, web hacking, SQL injection, and cryptography.

CEH v13 Tools: What Actually Matters for the Exam?

Do not memorize a massive CEH v13 tools list. Focus on tool purpose: reconnaissance, scanning, enumeration, vulnerability discovery, packet analysis, exploitation, web testing, wireless assessment, and cryptography. Official training provides exposure to thousands of tools.

CEH v13 Practical Exam

The CEH v13 Practical is a separate six-hour, hands-on assessment delivered in the iLabs Cyber Range. Candidates face 20 practical challenges involving tasks such as network scanning, vulnerability analysis, system hacking, web application attacks, and related security-audit activities.Passing the knowledge exam gives you CEH. Passing both the CEH knowledge exam and CEH v13 practical exam earns the CEH Master designation.

CEH v13 Certification Cost and Exam Voucher Price

The CEH v13 certification cost depends on whether you buy training or only an exam voucher. Current official pricing can change, but EC-Council presently lists the following:

ItemCurrent Listed Price
CEH exam voucher – remote RPS$950
CEH exam voucher – Pearson VUE$1,199
On-demand certification courseStarting at $1,699
Live online certification courseStarting at $2,499

If you plan to buy CEH v13 exam voucher access directly, note that the official vouchers are non-transferable and valid for one year from release.For searches such as CEH v13 exam cost in India, avoid relying on a fixed INR figure from an old blog. EC-Council says training pricing varies by region and delivery format; taxes, exchange rates, authorized training-center bundles, and promotions can change the final amount.

How to Get CEH v13 Certified

There are two main eligibility paths. Candidates who complete official EC-Council training can become eligible through that route. Candidates who skip official training can use the experience-based application path; EC-Council states that candidates should have two years of IT security experience or complete official training.A practical certification path is:

  1. Confirm eligibility through official training or the experience-based application.
  2. Study the current CEH v13 course outline and official blueprint.
  3. Build hands-on familiarity with scanning, enumeration, exploitation, web security, cloud, and defensive countermeasures.
  4. Use timed practice to prepare for 125 questions in four hours.
  5. Schedule and pass the CEH knowledge exam.
  6. Take the optional CEH Practical if your goal is CEH Master.

Best CEH v13 Study Strategy

A strong preparation plan should follow exam weight rather than textbook order. Spend the most time on Network and Perimeter Hacking, followed by Reconnaissance, System Hacking, and Web Application Hacking. Practice interpreting outputs and scenarios instead of memorizing tool names.Use the CEH v13 blueprint as your checklist, the official courseware as your knowledge source, labs for skill reinforcement, and mock exams for time management. For each topic, be able to answer four questions: What is the attack? How is it performed? How is it detected? How is it mitigated?

Is CEH v13 Worth It in 2026?

CEH v13 fits aspiring ethical hackers, cybersecurity analysts, network/security engineers, vulnerability analysts, SOC professionals, and IT professionals seeking structured offensive-security skills. EC-Council continues to identify Version 13 as the current release.For certification, prepare for the 312-50 knowledge exam first. For stronger hands-on validation, continue to CEH Practical and CEH Master. Combine blueprint-driven study, labs, and scenario-based practice rather than passive reading.
15Aug

PCI Certification from ASIS International is a professional credential for experienced investigators who want independent validation of their skills in case management, investigative techniques, evidence handling, and case presentation.

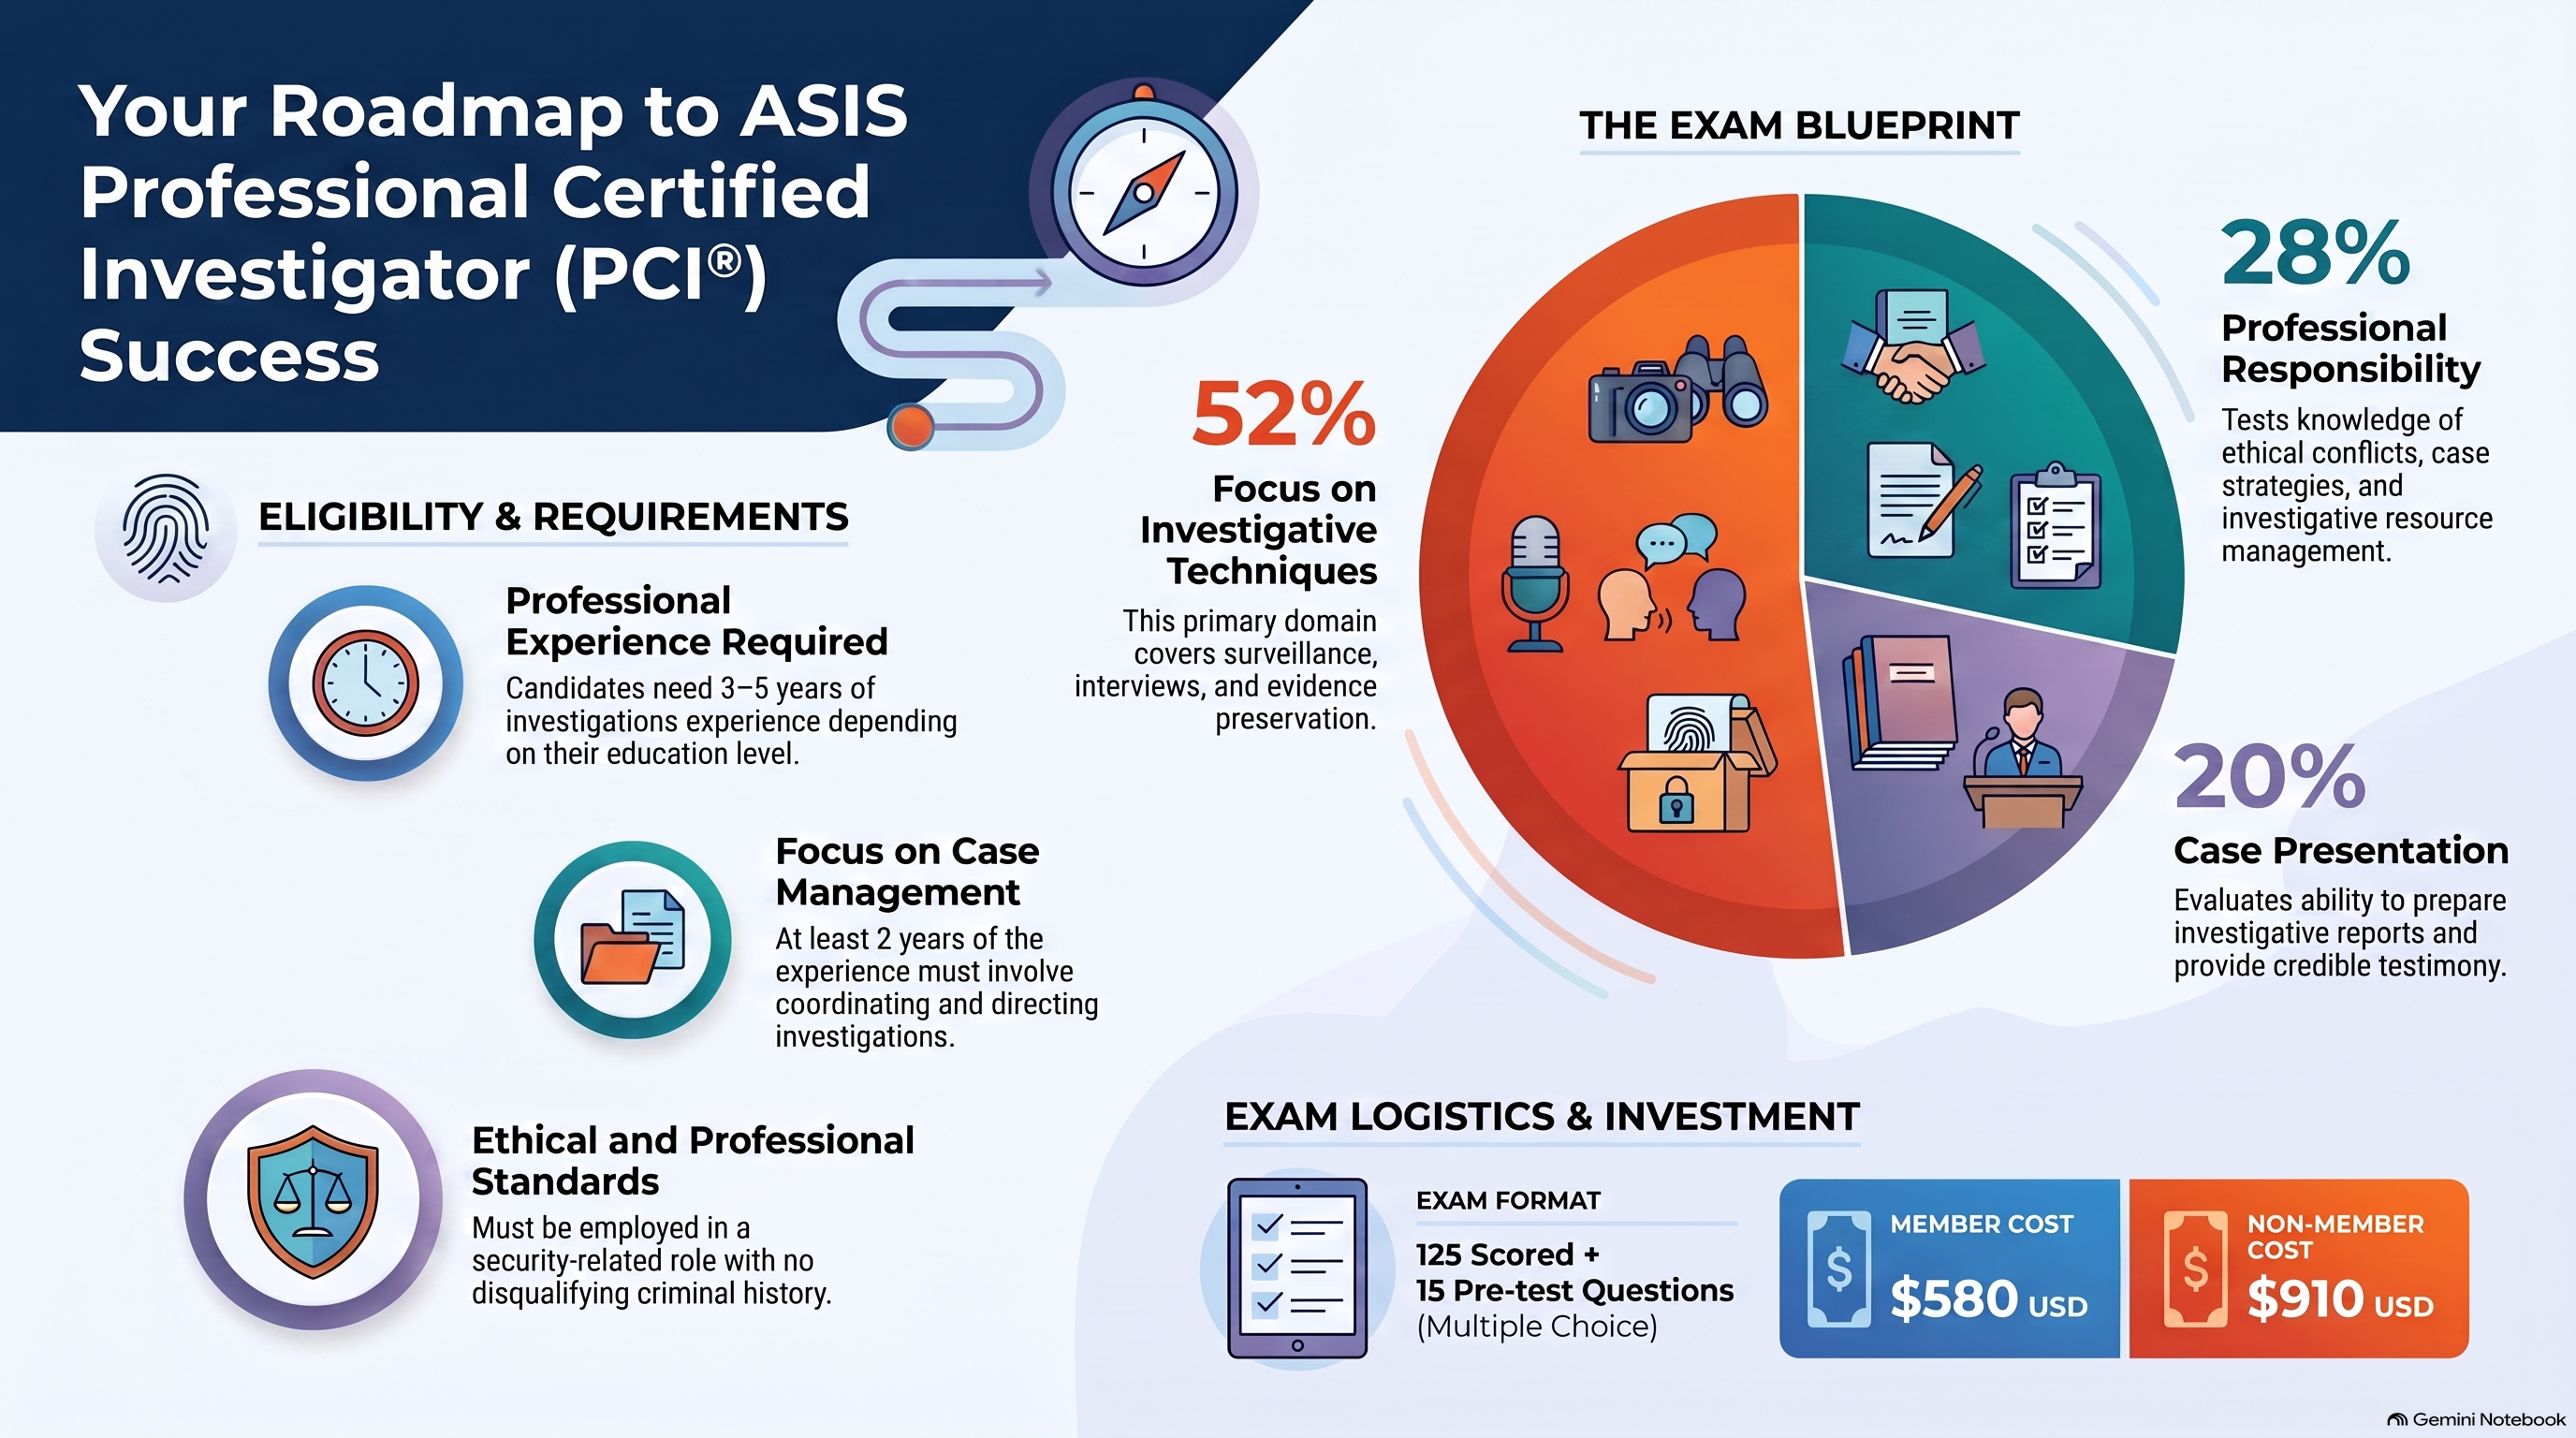
PCI Certification from ASIS International is a professional credential for experienced investigators who want independent validation of their skills in case management, investigative techniques, evidence handling, and case presentation. Officially called the Professional Certified Investigator (PCI®), it requires three to five years of investigations experience depending on education, including at least two years in case management. Candidates must pass a 140-question exam covering three domains and maintain the credential through continuing professional education during each three-year certification cycle with ASIS.

What Is the ASIS PCI Certification?

The Professional Certified Investigator PCI credential is a board certification offered by ASIS International for professionals whose work involves investigations, case management, evidence collection, investigative techniques, reporting, and testimony.Unlike an introductory investigation course, the ASIS PCI Certification is experience-based. ASIS specifically notes that candidates are expected to apply professional experience when answering exam questions rather than relying only on memorization.The credential is particularly relevant to professionals working in areas such as:

  • Corporate investigations

  • Fraud investigations

  • Loss prevention

  • Workplace investigations

  • Digital and high-tech crime

  • Insurance investigations

  • Forensics

  • Threat assessment

  • White-collar crime

  • Healthcare fraud

  • Public-sector investigations

ASIS states that its board certification programs are accredited by the ANSI National Accreditation Board (ANAB) against ISO/IEC 17024, providing an important distinction between professional certification and a simple training certificate.

Is ASIS PCI the Same as PCI Security Certification?

No. This is an important distinction.The ASIS PCI Certification means Professional Certified Investigator (PCI®) and focuses on professional investigations.It should not be confused with payment-card security programs associated with the PCI Security Standards Council, which develops standards related to protecting payment-card data.Therefore, when someone searches for PCI Security Certification, they should first determine whether they mean:

  • ASIS PCI®: Professional investigation and case-management certification.

  • Payment-card PCI programs: Credentials and programs associated with payment-card security standards.

For security investigators, corporate investigators, loss-prevention specialists, fraud professionals, and investigative managers, the ASIS credential is the relevant PCI Certification for individuals.

PCI Certification Exam Details

The current ASIS PCI exam contains 140 multiple-choice questions: 125 scored questions and 15 unscored pretest questions. Candidates receive 2.5 hours to complete the examination. A scaled score of 650 or higher is required to pass; this is a scaled score rather than a raw percentage of correct answers.

Exam DetailASIS PCI Information
CertificationProfessional Certified Investigator (PCI®)
ProviderASIS International
Exam FormatMultiple choice
Total Questions140
Scored Questions125
Unscored Questions15
Exam Time2.5 hours
Main Domains3
Passing Score650 scaled score
Testing OptionsPrometric test center or remote proctoring
Exam AvailabilityYear-round

ASIS currently permits candidates to test either at a Prometric testing center or remotely through Prometric's ProProctor platform. Exams are offered year-round after the candidate has been approved and receives authorization to test.

ASIS PCI Certification Exam Domains

The current examination blueprint places the greatest emphasis on actual investigative techniques and procedures.

PCI Exam DomainWeight
Professional Responsibility28%
Investigative Techniques & Procedures52%
Case Presentation20%

Domain I: Professional Responsibility — 28%

This domain evaluates your ability to manage investigations professionally and ethically. Topics include ethical conflicts, legal and organizational requirements, investigative planning, case strategy, resource management, risks, documentation, case closure, OSINT, and investigative process improvement.

Domain II: Investigative Techniques & Procedures — 52%

This is the largest portion of the exam and deserves the greatest preparation time.Candidates are tested on areas including:

  • Physical and electronic surveillance

  • Interview techniques

  • Indicators of deception

  • Evidence collection

  • Evidence preservation

  • Chain of custody

  • Digital and physical research

  • Open-source and proprietary information

  • Agency collaboration

  • Forensic techniques

  • Undercover investigations

  • Threat and risk assessments

  • Confidential sources

Domain III: Case Presentation — 20%

This domain focuses on converting investigative work into defensible findings. Candidates need to understand investigative report structure, confidentiality considerations, logical presentation of information, preparation for testimony, and testimony in administrative, civil, and criminal proceedings.

PCI Certification Requirements

The PCI Certification Requirements depend partly on your education. However, every pathway requires at least two years of case-management experience.

EducationInvestigation Experience Required
No higher education degree5 years
Bachelor's degree or equivalent4 years
Master's degree or equivalent3 years

Candidates who already hold the ASIS APP® may qualify for reduced experience requirements in some pathways. For example, an APP holder without a higher education degree may qualify with four years of investigation experience, while an APP holder with a bachelor's degree may qualify with three years.ASIS defines case management as coordinating and directing an investigation using relevant disciplines and resources so that the findings can be evaluated as a complete investigation.Additional eligibility expectations include qualifying full-time security-related employment experience, compliance with the ASIS Certification Code of Conduct, and agreement to certification program policies.

ASIS PCI Certification Cost in 2026

The current ASIS PCI Certification Cost varies according to ASIS membership and eligible emerging-market pricing.

Candidate CategoryPCI Exam Fee
ASIS Member$580
Member — Emerging Market 1$480
Member — Emerging Market 2$460
Nonmember$910
Nonmember — Emerging Market 1$720
Nonmember — Emerging Market 2$680

The current standard PCI Certification Cost therefore ranges from $580 for an ASIS member to $910 for a nonmember, before optional training or study resources. ASIS states that study materials are recommended but purchased separately.The retake fee for PCI is currently $480 for standard member and nonmember candidates, with lower designated emerging-market rates. Candidates may attempt the examination up to three times within their one-year eligibility period, with at least 60 days between attempts.

How to Get PCI Certification

The PCI Certification Process is more than simply registering for an exam.

  1. Confirm your eligibility.
    Verify that your education, investigation experience, and minimum two years of case-management experience satisfy ASIS requirements.

  2. Prepare your documentation.
    ASIS may require an applicable education transcript, a résumé or CV showing relevant experience, three professional references, and supervisor information for employment verification.

  3. Submit your online application.
    ASIS states that application review normally takes approximately two to three weeks.

  4. Receive authorization to test.
    Once approved, you receive your ASIS eligibility ID and exam-scheduling instructions.

  5. Schedule through Prometric.
    Choose either a testing center or an eligible remotely proctored examination.

  6. Prepare using the current domains.
    Your study plan should reflect the 28% / 52% / 20% exam weighting rather than treating every topic equally.

  7. Pass the examination.
    A scaled score of 650 or higher is required.

This is the practical answer to How to Get PCI Certification: meet the experience requirements first, document them correctly, obtain ASIS approval, and then pass the examination.

How Should You Approach PCI Certification Training?

Effective PCI Certification Training should be domain-driven and scenario-focused.A common mistake is spending equal time on every domain. Since Investigative Techniques & Procedures represents 52% of the examination, it should generally receive the largest share of study time.A stronger preparation strategy is to:

  • Map your experience against every official exam task.

  • Identify domains where your job gives you limited exposure.

  • Study the official reference materials.

  • Practice scenario-based decision making.

  • Review evidence and chain-of-custody procedures carefully.

  • Practice investigative reporting and testimony concepts.

  • Complete timed practice questions.

  • Analyze why incorrect options are wrong rather than memorizing answers.

ASIS recommends Protection of Assets – Investigations and the Investigations Standard among the primary reference materials and also offers study guides, flash cards, practice tests, and review courses. ASIS emphasizes that the examination is experience-based and specifically warns candidates not to rely solely on memorization.

Is the Professional Certified Investigator PCI Certification Worth It?

For experienced investigators, the credential can provide a clear way to validate skills that may otherwise be difficult to demonstrate on a résumé.ASIS identifies benefits including professional recognition, validation of investigative expertise, career differentiation, and increased professional credibility.The credential is particularly relevant if your responsibilities include managing investigations rather than simply participating in isolated investigative tasks.A fraud investigator who regularly handles interviews but has limited responsibility for evidence management, for example, should strengthen knowledge of chain of custody, evidence preservation, case strategy, and reporting before attempting the exam. Conversely, an experienced case manager may need additional preparation in digital research, surveillance, or forensic concepts.That difference is why PCI preparation should begin with a skills-gap analysis, not simply a collection of practice questions.

Maintaining Your PCI Certification

Passing the exam is not the end of the certification process.ASIS requires certificants to earn 60 Continuing Professional Education (CPE) hours during each three-year certification cycle to maintain their credential. Qualifying activities can include relevant education, teaching, professional service, authorship, volunteering, and other approved professional-development activities.This continuing-education requirement helps distinguish a professional certification from a one-time course completion certificate.

Who Should Pursue PCI Certification?

The Professional Certified Investigator PCI Certification is best suited to experienced professionals whose responsibilities involve:

  • Corporate or internal investigations

  • Fraud and financial investigations

  • Loss prevention

  • Security investigations

  • Workplace misconduct investigations

  • Investigative case management

  • Evidence collection and preservation

  • Investigative reporting

  • Interviewing and surveillance

  • Investigation leadership

It is not an entry-level certification. If you do not yet meet the required investigation and case-management experience, building relevant professional experience should come before intensive exam preparation.

Your Next Step Toward ASIS PCI Certification

Start by comparing your experience against the official PCI Certification Requirements, especially the two-year case-management requirement. Then evaluate yourself against the three exam domains: Professional Responsibility (28%), Investigative Techniques & Procedures (52%), and Case Presentation (20%).Once your eligibility is clear, build a structured preparation plan around your weakest domains rather than studying every topic equally. That approach makes your ASIS PCI certification preparation more focused, measurable, and aligned with what the examination actually evaluates.


The CompTIA Security+ certification is a vendor-neutral cybersecurity credential that validates practical baseline skills in threat analysis, secure architecture, security operations, identity, risk, and incident response. The current exam is SY0-701, with up to 90 multiple-choice and performance-based questions in 90 minutes; a score of 750 on a 100–900 scale is required to pass. It suits aspiring and early-career security professionals, IT administrators, and technicians who want structured proof of job-ready security knowledge and a recognized cybersecurity foundation for employers.

What Is CompTIA Security+?

CompTIA Security+ is designed to verify that a candidate can understand security problems and apply appropriate controls rather than simply memorize cybersecurity terminology.Unlike certifications tied to a specific firewall, cloud platform, or security product, CompTIA Security focuses on vendor-neutral principles. Candidates learn how organizations protect systems, identities, networks, cloud environments, applications, and sensitive information.The current security+ certification exam is SY0-701, which measures skills across five cybersecurity domains. The certification is especially relevant for professionals who need a broad technical foundation before moving toward areas such as SOC operations, cybersecurity analysis, penetration testing, security engineering, cloud security, or governance.A useful way to think about security plus is that it sits between basic IT knowledge and specialist cybersecurity expertise. It expects candidates to understand networking and systems while also knowing how security controls affect real operational environments.

CompTIA Security+ Exam Details

Candidates earn the comptia security+ certification by passing one examination.

Exam DetailCurrent SY0-701 Information
Exam CodeSY0-701
Maximum QuestionsUp to 90
Exam Duration90 minutes
Question TypesMultiple-choice and performance-based questions
Passing Score750 on a 100–900 scale
Experience RequirementNo mandatory prerequisite
Recommended BackgroundNetwork+ knowledge and about two years of IT administration experience with a security focus
Certification CycleThree years

The CompTIA Security+ exam includes performance-based questions, commonly called PBQs. These matter because they require candidates to interpret situations, configure or analyze security controls, and solve practical problems rather than select definitions from memory.That changes how candidates should approach comptia security exam preparation: knowing what a firewall, certificate, SIEM, or access-control model does is not enough. You should also understand when and why you would deploy it.

What Does the Security+ SY0-701 Exam Cover?

The CompTIA Security Plus exam is divided into five domains.

SY0-701 DomainExam Weight
General Security Concepts12%
Threats, Vulnerabilities, and Mitigations22%
Security Architecture18%
Security Operations28%
Security Program Management and Oversight20%

These percentages should influence your study plan. Security Operations represents 28% of the exam, making it the largest domain, while threats and vulnerabilities plus security program management together account for another 42%.

General Security Concepts

This section establishes the principles behind security+ technologies and controls, including:

  • Confidentiality, integrity, and availability
  • Authentication and authorization
  • Zero Trust principles
  • Physical and logical security controls
  • Cryptography
  • Public key infrastructure
  • Change management

Strong candidates connect these concepts instead of learning isolated definitions.

Threats, Vulnerabilities, and Mitigations

This domain focuses on identifying how attacks happen and selecting appropriate defenses.Topics include:

  • Malware and ransomware
  • Social engineering
  • Password attacks
  • Network attacks
  • Application vulnerabilities
  • Indicators of compromise
  • Vulnerability assessment
  • Threat mitigation

For effective security plus training, practice identifying the difference between the attack itself, the vulnerability that enabled it, and the control that reduces the risk.

Security Architecture

Security architecture examines how systems should be designed securely across:

  • Cloud environments
  • Virtualization
  • Enterprise infrastructure
  • Network segmentation
  • Data protection
  • High availability
  • Resilience and recovery

A strong CompTIA Security Plus course should show how these technologies interact rather than teaching them as unrelated terms.

Security Operations

This is the largest SY0-701 domain.Candidates need practical familiarity with:

  • System hardening
  • Asset management
  • Vulnerability management
  • Security monitoring
  • Firewalls and IDS/IPS
  • Endpoint protection
  • Identity and access management
  • Incident response
  • Digital evidence
  • Security automation

Because of its weight, this should receive substantial attention in any security+ training program.

Security Program Management and Oversight

The final domain moves beyond technical controls into organizational cybersecurity.It covers:

  • Risk management
  • Security policies
  • Compliance
  • Audits
  • Vendor risk
  • Security awareness
  • Business continuity
  • Governance

Understanding these areas helps technical professionals see why organizations implement controls—not merely how those controls work.

How Much Does CompTIA Security+ Cost?

As of August 2026, the U.S. list price for a single security plus voucher is approximately $439, following a CompTIA pricing increase that took effect in June 2026. Regional pricing, taxes, academic eligibility, promotions, partner discounts, and bundles can change the final amount.Therefore, searches for security plus certification cost, comptia security cost, comptia security plus cost, comptia security exam cost, comptia security+ exam cost, or how much does comptia security cost should not be answered with an old fixed figure.Your actual CompTIA Security certification cost may include:

  1. The examination voucher
  2. Study resources
  3. Practice examinations
  4. Hands-on labs
  5. Instructor-led training, if selected
  6. A retake option or additional voucher if required

A CompTIA Security Plus voucher or CompTIA Security voucher normally represents exam access rather than a complete preparation package. Candidates should compare what is included before purchasing bundles.

Who Should Take the CompTIA Security+ Certification?

The certification can be valuable for:

  • Aspiring cybersecurity professionals
  • Help desk technicians moving into security
  • Network administrators
  • System administrators
  • SOC analyst candidates
  • Security administrators
  • IT auditors
  • Cloud and infrastructure professionals
  • Technical support professionals
  • Professionals beginning a cybersecurity career

There is no mandatory experience prerequisite, although CompTIA recommends Network+ knowledge and approximately two years of IT administration experience with a security focus.Beginners can still pursue comptia security+, but candidates without networking fundamentals should first become comfortable with TCP/IP, ports, protocols, operating systems, authentication, routing, and common infrastructure technologies.

What Should CompTIA Security+ Training Include?

A quality CompTIA Security training program should go beyond slides and vocabulary.Look for security plus certification training that includes:

  • Coverage aligned with SY0-701 objectives
  • Instructor explanation of difficult concepts
  • Scenario-based questions
  • Performance-based question preparation
  • Security configuration exercises
  • Network security labs
  • Incident-response scenarios
  • Vulnerability analysis
  • Timed mock examinations
  • Weak-domain analysis

A security plus course, CompTIA Security Plus training, or CompTIA Security+ training course should teach candidates to choose the best security response under specific conditions.That decision-making skill is frequently more valuable than memorizing hundreds of acronyms.

Online Course vs. Self-Study vs. Instructor-Led Training

A security plus online course works well for candidates who need flexibility, while instructor-led CompTIA Security Plus certification training can help learners who benefit from structured explanations and accountability.Self-study may be sufficient if you already manage networks, Windows/Linux systems, identity platforms, firewalls, or security tooling.Structured CompTIA Security+ course preparation may be more useful when:

  • You are entering cybersecurity from another field.
  • Networking concepts are still unfamiliar.
  • You struggle with scenario-based questions.
  • You need a fixed study schedule.
  • You want guided PBQ preparation.

The best CompTIA Security course is not necessarily the longest. It is the one that converts exam objectives into skills you can apply.

How to Prepare for the CompTIA Security+ Exam

Use a layered preparation strategy:

  1. Download the current SY0-701 objectives and use them as your checklist.
  2. Take a diagnostic assessment before intensive study.
  3. Study by domain, giving additional time to Security Operations.
  4. Build hands-on understanding of firewalls, permissions, logs, certificates, command-line tools, vulnerabilities, and incident response.
  5. Practice scenario-based questions, not only definition questions.
  6. Complete timed mock exams under the 90-minute limit.
  7. Review incorrect answers by objective, not simply by question.
  8. Schedule the exam only when your performance is consistently stable.

This approach makes CompTIA Security+ certification training more targeted because preparation is driven by measurable weaknesses rather than the number of study hours completed.

Is Security+ Worth It?

The security plus certification is strongest when treated as a foundation, not a career shortcut.It can validate baseline cybersecurity knowledge and provide a structured pathway into security-focused roles, but certification alone does not replace practical experience. Pair it with labs, home projects, troubleshooting experience, cloud environments, log analysis, and security tools.That combination demonstrates something employers value more than a credential by itself: the ability to recognize a security problem, understand its risk, and choose a defensible technical response.Security+ credentials earned under CompTIA's continuing education program are generally valid for three years, and Security+ renewal requires 50 CEUs when following the continuing education route.

Your Next Step: Prepare for SY0-701, Not Just the Certificate

If your goal is to earn the CompTIA Security+ certification, build your preparation around the actual SY0-701 objectives, performance-based tasks, and real security scenarios.Choose a CompTIA Security+ certification course that helps you understand why a control is appropriate, practice applying it, identify your weak domains, and perform accurately under exam conditions. That preparation gives the security plus certification greater value because you finish with more than an exam result—you develop a cybersecurity foundation you can continue building on.

14Aug

CIA Certification is the Certified Internal Auditor credential awarded by The Institute of Internal Auditors (The IIA) to professionals who demonstrate competence in internal audit fundamentals, engagement work, and audit-function management.

CIA Certification is the Certified Internal Auditor credential awarded by The Institute of Internal Auditors (The IIA) to professionals who demonstrate competence in internal audit fundamentals, engagement work, and audit-function management. The traditional route requires passing three computer-based exam parts and meeting education/experience requirements. In 2026, Part 1 has 125 questions in 150 minutes; Parts 2 and 3 each have 100 questions in 120 minutes. Candidates must also satisfy ethics, identification, and experience-verification requirements before certification within the program window.

What Is CIA Certification?

The Certified Internal Auditor (CIA) is a professional internal audit credential administered by The Institute of Internal Auditors. The IIA describes the CIA as the only globally recognized certification specifically for internal auditors and reports more than 220,000 CIAs across 170 countries.The credential validates the ability to understand and apply internal audit principles across governance, risk management, controls, fraud, engagement planning, audit evidence, reporting, quality, and management of an internal audit function.A useful distinction: a CIA certification course prepares you for the examinations, but the training provider does not award the credential. The IIA Certified Internal Auditor designation is awarded only after The IIA's examination and program requirements have been satisfied.The phrase “CIA Certified Internal Auditor” is technically redundant because CIA already means Certified Internal Auditor. In professional profiles, the standard designation is simply CIA after the holder's name.

Who Should Consider the CIA?

The IIA CIA certification is especially relevant for professionals working in or moving toward:

  • Internal auditing

  • Risk management

  • Governance

  • Compliance

  • Internal controls

  • External audit

  • Quality assurance

  • Audit and assessment functions

  • Finance and assurance leadership

It is not limited to people who already hold an internal auditor job title. The IIA recognizes several related areas as equivalent professional experience, including risk management, compliance, external audit, quality assurance, internal control, and audit/assessment disciplines.For beginners, The IIA also offers the Internal Audit Practitioner (IAP) pathway. Candidates can earn the IAP through CIA Part 1 and, while the IAP remains active, receive a waiver for Part 1 when progressing to the CIA program.

CIA Certification Requirements and Eligibility

The CIA certification requirements combine education or an approved entry pathway, examinations, professional experience, identification, ethics, and completion within the program eligibility period.For candidates researching certified internal auditor requirements, certified internal auditor certification requirements, or the requirements for CIA certification, the education-to-experience relationship is particularly important.

Entry RouteExam RequirementExperience Needed for Certification
Master's degree or equivalentPass all 3 parts1 year
Bachelor's degree or equivalentPass all 3 parts2 years
Active IAP holderPart 1 waiver; pass Parts 2 & 3Up to 5 years, depending on education
5 years of qualifying internal audit experience or equivalentPass all 3 partsNo additional experience under this handbook route

The IIA allows degree-qualified candidates to sit for exams before completing the required professional experience. They cannot, however, receive the designation until all program requirements have been satisfied. Candidates generally have three years from acceptance into the CIA program to complete the requirements.Therefore, CIA certification eligibility and certified internal auditor eligibility should be checked before paying for an exam preparation package.

CIA Certification Exam Structure

The traditional CIA certification exam consists of three separate multiple-choice examinations. Candidates are not required to take the parts in numerical order.

CIA Exam PartCurrent TitleQuestionsTime
Part 1Internal Audit Fundamentals125150 minutes
Part 2Internal Audit Engagement100120 minutes
Part 3Internal Audit Function100120 minutes

The certified internal auditor exam uses scaled scoring, with 600 required to pass.

CIA Part 1: Internal Audit Fundamentals

The current syllabus emphasizes four areas:

  • Foundations of Internal Auditing – 35%

  • Ethics and Professionalism – 20%

  • Governance, Risk Management, and Control – 30%

  • Fraud Risks – 15%

Part 1 establishes the conceptual foundation for professional internal auditing, including independence, objectivity, assurance and advisory services, governance, risk, controls, fraud, and professional conduct.

CIA Part 2: Internal Audit Engagement

Part 2 moves from principles to executing actual audit engagements:

  • Engagement Planning – 50%

  • Information Gathering, Analysis, and Evaluation – 40%

  • Engagement Supervision and Communication – 10%

The updated syllabus integrates practical areas such as cybersecurity, IT controls, data analytics, artificial intelligence, machine learning, robotic process automation, finance, business processes, and evidence evaluation into engagement scenarios.

CIA Part 3: Internal Audit Function

Part 3 focuses more heavily on managing and communicating the work of an internal audit function:

  • Internal Audit Operations – 25%

  • Internal Audit Plan – 15%

  • Quality of the Internal Audit Function – 15%

  • Engagement Results and Monitoring – 45%

This progression is important for effective CIA exam preparation: Part 1 asks whether you understand internal auditing, Part 2 tests how you perform engagements, and Part 3 increasingly tests how audit activity is managed, communicated, monitored, and improved.

CIA Exam Cost in 2026

The official CIA exam cost depends primarily on IIA membership status.

FeeIIA MemberNon-Member
CIA Application$120$240
Part 1$310$445
Part 2$280$415
Part 3$280$415
Total official application + exam fees$990$1,515

These amounts represent the core CIA certification cost before study materials, membership dues, taxes, retakes, rescheduling, extensions, or training expenses. The IIA notes that pricing may differ in countries where certification services operate through National Institutes.So whether someone searches for the cost of CIA certification, certified internal auditor certification cost, certified internal auditor cost, or certified internal auditor exam cost, the key distinction is between mandatory IIA fees and optional preparation expenses.

How to Become a Certified Internal Auditor

The process is more straightforward when treated as a sequence rather than simply “study and take an exam.”

  1. Confirm your eligibility. Determine which education, IAP, experience, or accelerated pathway applies.

  2. Create or access your CCMS account. The Certification Candidate Management System manages the application.

  3. Submit the CIA application and supporting documents.

  4. Wait for application approval. Exam registration is not available until the required documentation is approved.

  5. Register and schedule each CIA exam part.

  6. Prepare according to the current syllabus rather than relying solely on old question banks.

  7. Pass all required exam parts.

  8. Complete experience verification.

  9. Receive the CIA designation and maintain it through applicable annual renewal and CPE requirements.

How to Approach CIA Exam Preparation

Strong certified internal auditor exam preparation should focus on decision-making, not memorizing definitions.Build study sessions around three layers:Concept → application → judgment.For example, knowing what auditor independence means is only the first layer. You should also be able to recognize an impairment in a scenario and determine the most appropriate action by the auditor, chief audit executive, senior management, or board.A quality CIA certification training program should therefore provide:

  • Current syllabus-aligned instruction

  • Scenario-based practice questions

  • Detailed rationales for correct and incorrect answers

  • Timed mock examinations

  • Performance analysis by syllabus area

  • Revision planning based on weak domains

  • Instructor support for difficult judgment-based concepts

The same criteria apply when evaluating a certified internal auditor course, certified internal auditor online course, or other CIA certification online preparation option.

What Changed in the Modern CIA Exam?

Candidates using older preparation material should be careful. The current CIA syllabus is more tightly aligned with modern internal audit practice and the Global Internal Audit Standards.Technology and business knowledge are increasingly tested in context. Instead of treating IT, cybersecurity, analytics, accounting, or business knowledge as isolated theory, candidates may encounter them while planning engagements, analyzing evidence, evaluating controls, or managing audit work.There is also a language-specific transition detail in 2026: The IIA states that some language versions, including Arabic and Simplified Chinese, transition to the newer syllabus on different schedules. Candidates should therefore verify the syllabus applicable to their exam language before beginning serious preparation.

Is the CIA Certification Worth Pursuing?

For professionals committed to CIA internal audit, assurance, governance, controls, or risk careers, the credential provides something a general accounting or business qualification cannot: specialized validation of professional internal audit competence.The strongest value comes when certification is combined with real engagement experience—planning audits, assessing controls, evaluating evidence, communicating findings, understanding organizational risk, and working with management and boards.The CIA is an Institute of Internal Auditors certification, not simply an exam badge. That distinction matters because the designation combines examination performance, professional requirements, ethics, experience, and continuing development.

Your Next Step Toward the CIA

Start by checking your eligibility and identifying which pathway applies to you. Then download the current syllabus for each required part and build your study plan around its actual weighting.If you choose a CIA certification course, prioritize current syllabus coverage, realistic question practice, explanations that teach why an answer is correct, and measurable mock-exam readiness. Good preparation should not simply help you remember internal audit terminology—it should train you to make the professional judgments the CIA exam is designed to test.


The CompTIA Network+ certification validates practical networking skills across connectivity, infrastructure, operations, security, and troubleshooting. The current exam is N10-009, with up to 90 questions, 90 minutes, and a passing score of 720/900. Its five domains are Networking Concepts, Network Implementation, Network Operations, Network Security, and Network Troubleshooting. The certification is useful for beginners and IT professionals targeting network support, systems administration, and security-related roles. CompTIA recommends hands-on networking experience before attempting the exam.

What Is CompTIA Network+ Certification?

CompTIA Network+ certification is a vendor-neutral credential designed to demonstrate that a candidate understands how computer networks are implemented, operated, secured, and troubleshot.Unlike certifications tied to one manufacturer's equipment, Network+ focuses on transferable networking concepts. That makes it useful for people who may eventually work with Cisco, Microsoft, Juniper, cloud platforms, security products, or mixed-vendor environments.The current version is CompTIA Network+ N10-009. It was introduced in June 2024 and replaced the previous N10-008 exam. The current objectives place particular emphasis on troubleshooting, network operations, modern infrastructure, cloud connectivity, virtualization, security, and physical network implementation.For someone asking what is CompTIA Network+, the simplest answer is: it is a vendor-neutral networking certification that tests whether you can understand and work with real-world network infrastructure.

CompTIA Network+ Exam at a Glance

Exam DetailCurrent Information
CertificationCompTIA Network+
Current examN10-009
Maximum questions90
Exam duration90 minutes
Question typesMultiple-choice and performance-based
Passing score720/900
DeliveryPearson VUE testing center or online proctored
Recommended experience9–12 months of networking experience
Main domains5

The N10-009 exam contains a maximum of 90 questions and combines conventional questions with performance-based tasks.

CompTIA Network+ Exam Objectives

Knowing the CompTIA Network+ objectives is more useful than simply collecting study materials. The N10-009 blueprint divides the exam into five domains:

DomainExam Weight
Networking Concepts23%
Network Implementation20%
Network Operations19%
Network Security14%
Network Troubleshooting24%

The distribution reveals an important preparation strategy: troubleshooting and networking concepts together account for 47% of the exam. Candidates who spend equal study time on every topic may therefore be using their preparation hours inefficiently.

1. Networking Concepts

This domain establishes the technical foundation. Topics include:

  • OSI and TCP/IP models
  • Network topologies
  • IPv4 and IPv6
  • Ports and protocols
  • Transmission technologies
  • Network appliances
  • Wireless concepts
  • Cloud networking
  • Virtual networking
  • Network services

You should be able to explain not only what a technology does but also why one solution would be selected over another.

2. Network Implementation

Network implementation focuses on deploying infrastructure.Study areas include:

  • Switching
  • Routing
  • Wireless technologies
  • Ethernet standards
  • Network devices
  • Physical installations
  • VLAN-related concepts
  • Routing technologies
  • Network design considerations

The practical question behind this domain is simple: can you translate a network requirement into an appropriate technical implementation?

3. Network Operations

The Network Operations domain covers the ongoing management of infrastructure.Expect concepts involving:

  • Network documentation
  • Monitoring
  • Configuration management
  • Business continuity
  • Disaster recovery
  • Change management
  • Network services
  • Performance monitoring

This is particularly relevant to candidates targeting network support and administration roles.

4. Network Security

Security represents 14% of the N10-009 objectives. Important concepts include network hardening, secure configurations, authentication, segmentation, common attacks, and security architecture.The key mistake is treating security as a separate subject. In real environments, security decisions affect routing, wireless access, identity, segmentation, remote connectivity, and troubleshooting.

5. Network Troubleshooting

At 24%, troubleshooting is the largest N10-009 domain.Candidates should practice structured diagnosis rather than memorizing isolated answers.A useful troubleshooting process is:

  1. Identify the problem.
  2. Establish a theory of probable cause.
  3. Test the theory.
  4. Create an action plan.
  5. Implement the solution.
  6. Verify functionality.
  7. Document the results.

Learn to interpret symptoms such as latency, packet loss, DNS failures, incorrect IP configuration, wireless interference, duplex problems, and routing issues.

CompTIA Network+ Exam Preparation Strategy

A strong CompTIA Network+ training plan should combine theory with hands-on work.

Step 1: Start With the Official Objectives

Review the current N10-009 objectives before choosing a course. Use them as a checklist rather than studying randomly.

Step 2: Build the Networking Foundation

Before attempting difficult troubleshooting questions, become comfortable with:

  • OSI layers
  • TCP/IP
  • IPv4 addressing
  • IPv6 basics
  • Subnetting
  • Ports
  • Protocols
  • DNS
  • DHCP
  • Routing
  • Switching

Step 3: Practice Configuration

A CompTIA Network+ certification training program becomes much more valuable when paired with practical labs.Build small environments using network simulators, virtual machines, or physical equipment. Configure addresses, test connectivity, inspect routes, and deliberately create failures.

Step 4: Use Practice Questions as Diagnostics

A CompTIA Network+ practice test should not be used simply to chase a percentage.For every incorrect answer, determine:

  • What concept did you misunderstand?
  • Was the question testing terminology or troubleshooting?
  • Why were the other choices incorrect?
  • Can you reproduce the underlying scenario in a lab?

This turns practice questions into a feedback mechanism.

CompTIA Network+ Study Guide: What Should It Include?

A useful CompTIA Network+ study guide should map directly to N10-009 objectives.Avoid resources that spend most of their time teaching outdated exam content. N10-009 introduced or expanded coverage involving areas such as SD-WAN, SDN, infrastructure as code, VxLAN, modern cloud networking, Zero Trust, SASE/SSE, and physical infrastructure concepts.A good study guide should therefore combine:Concept → Example → Configuration → Failure → TroubleshootingThat sequence is much closer to how networking knowledge is applied on the job.

CompTIA Network+ Training and Online Courses

There is no single best CompTIA Network+ online course for every learner.Choose a Network+ course based on how you learn:

  • Video course: useful for structured explanations.
  • Book/study guide: useful for detailed reference.
  • Hands-on labs: essential for practical understanding.
  • Practice exams: useful for measuring readiness.
  • Instructor-led training: useful when you need accountability and immediate feedback.

A strong CompTIA Network+ training course should cover the complete N10-009 objective list rather than focusing only on frequently memorized questions.

CompTIA Network+ Cost and Exam Voucher

The CompTIA Network+ cost depends on the purchasing option, region, taxes, promotions, and whether you buy an exam voucher alone or a bundle.Candidates should distinguish between:

  • CompTIA Network+ exam voucher
  • Exam voucher plus training
  • Voucher plus retake option
  • Third-party training costs
  • Practice-test subscriptions
  • Lab platforms

Because prices can change, verify the current amount before purchasing. Third-party listings can become outdated quickly.A CompTIA Network+ voucher can be useful when purchased through an authorized channel, but price should not be the only consideration. Compare what is included, particularly if you need training materials or a retake option.

CompTIA Network+ Practice Test: How to Use It Correctly

A CompTIA Network+ practice exam is most useful during the final stage of preparation.Don't memorize practice questions. The real exam can present the same concept in a different scenario.Instead, track performance by domain:

ResultRecommended Action
90%+Maintain and review weak areas
80–89%Continue targeted revision
70–79%Identify knowledge gaps
Below 70%Return to fundamentals before taking more mocks

These percentages are study benchmarks, not official CompTIA passing requirements.Performance-based questions deserve special attention because they test application rather than simple recognition.

CompTIA Network+ for Beginners

CompTIA Network+ for beginners is a practical starting point if you want broad networking knowledge without committing immediately to a vendor-specific platform.You do not need to be an experienced network engineer. However, basic familiarity with computers, operating systems, IP addressing, and troubleshooting will make the learning process easier.If networking is completely new, start with:

  1. Basic computer networking.
  2. IP addressing and subnetting.
  3. OSI and TCP/IP models.
  4. Ethernet and wireless.
  5. DNS and DHCP.
  6. Routing and switching.
  7. Security fundamentals.
  8. Troubleshooting labs.

Then move into full N10-009 preparation.

Jobs With CompTIA Network+

What can you do after earning Network+?Potential entry-level and intermediate paths include:

  • Network Support Technician
  • Network Administrator
  • IT Support Specialist
  • Systems Administrator
  • Network Technician
  • Technical Support Specialist
  • Junior Network Engineer
  • Infrastructure Support Technician

The certification itself does not guarantee employment. Employers still look for troubleshooting ability, communication skills, practical experience, and familiarity with the technologies used in their environment.That is why combining Network+ certification with hands-on labs can make your résumé stronger than listing the credential alone.

Should You Get Network+ Certification?

Network+ certification makes the most sense if you want a vendor-neutral foundation and plan to work with networks as part of an IT, infrastructure, cloud, or security career.It is particularly useful when you want to understand networking before moving toward specialized certifications.If your immediate goal is a specific vendor environment, a vendor-specific certification may eventually be more appropriate. But Network+ can provide the conceptual foundation needed to understand those technologies.

Your Next Step

Start with the N10-009 objectives, identify your weakest domains, and build your preparation around those gaps. Give extra attention to Networking Concepts (23%) and Network Troubleshooting (24%), then reinforce the material with labs and realistic practice questions.The goal should not be to memorize a Network+ exam question bank. It should be to reach the point where you can look at a network problem, identify the likely cause, test your theory, and explain why your solution works. That is the skill the certification is designed to measure.

CompTIA A+ Certification is an entry-level IT credential covering hardware, operating systems, networking, troubleshooting, security, and technical support. The current certification requires two exams: Core 1 (220-1201) and Core 2 (220-1202). It is designed for people starting or advancing in IT support roles and is especially useful for help desk, desktop support, field service, and technical support careers. Candidates should prepare against the current exam objectives rather than older 220-1101/220-1102 materials.

What Is CompTIA A+ Certification?

CompTIA A+ Certification is a vendor-neutral IT credential focused on practical technical support skills. Instead of training you for one manufacturer's technology, the certification covers a broad range of hardware, software, networking, troubleshooting, operating systems, security, and operational concepts. For beginners, that breadth is one of its biggest advantages. A person studying for CompTIA A+ learns how computers and common IT environments work before specializing in areas such as cybersecurity, networking, cloud computing, or systems administration. The certification is particularly relevant to roles such as help desk technician, IT support specialist, desktop support technician, field service technician, and technical support specialist.

CompTIA A+ Core 1 vs. Core 2

The current CompTIA A+ certification uses two separate exams. Candidates need to pass both rather than treating Core 1 as a standalone certification.

AreaCompTIA A+ Core 1CompTIA A+ Core 2
Exam220-1201220-1202
Main emphasisHardware, networking, mobile devices, virtualization and cloudOperating systems, security, software troubleshooting and operational procedures
PurposeTechnical foundationSupport, troubleshooting and security application
Certification requirementPass Core 1 and Core 2Pass Core 1 and Core 2

This two-exam structure matters when planning your CompTIA A+ certification training. Studying for both exams simultaneously can create unnecessary confusion. A better strategy is to build your foundation with Core 1 and then move into Core 2.

What Is CompTIA A+ Core 1 (220-1201)?

CompTIA A+ Core 1, identified as 220-1201, concentrates heavily on the physical and infrastructure side of IT support. The CompTIA A+ 220-1201 objectives include areas involving mobile devices, networking technology, hardware, virtualization and cloud concepts, and hardware and network troubleshooting. For example, a technician may need to understand why a computer fails to boot, how a storage device should be replaced, why wireless connectivity is unreliable, or which hardware component is appropriate for a particular requirement. A strong Core 1 preparation strategy therefore involves more than reading definitions. Candidates should understand what components do, how they interact, and how symptoms can be used to narrow down a technical problem.

What Is CompTIA A+ Core 2 (220-1202)?

Core 2, or 220-1202, moves further into operating systems, security, software troubleshooting, and operational procedures. Candidates should understand common operating-system environments, security fundamentals, troubleshooting methodology, and professional IT practices. This part of the CompTIA A+ certification exam is particularly relevant to help desk and desktop-support scenarios because technicians frequently troubleshoot user accounts, software problems, permissions, malware-related issues, configuration problems, and operating-system failures. The important distinction is that Core 2 is not simply "the security exam." Security is one component of a broader technical-support curriculum.

CompTIA A+ Exam Objectives: What Should You Study?

The current CompTIA A+ exam objectives should be your primary checklist when building a study plan.Use the objectives to create a gap analysis:

  1. Download or obtain the current official objectives.
  2. Mark topics you already understand.
  3. Identify unfamiliar terminology.
  4. Separate knowledge gaps from hands-on skill gaps.
  5. Practice the weak areas.
  6. Re-test yourself without looking at the answers.
  7. Review the objectives again before scheduling the exam.

This is more efficient than studying an enormous collection of unrelated CompTIA A+ study material. One important rule: verify the exam version before purchasing a study guide or practice exam. Older 1100-series resources may not accurately reflect the current 1200-series objectives.

CompTIA A+ Certification Training: What Actually Helps?

A good CompTIA A+ certification training course should teach you how to troubleshoot rather than simply memorize terminology. Look for training that combines explanations with practical exercises. For example, when studying memory, don't stop at learning what RAM is. Understand how insufficient memory can affect performance, how to identify compatible modules, and how a technician would diagnose a suspected memory problem. The same principle applies to networking. Learn what an IP address, DNS, DHCP, gateway, switch, router, and wireless access point do, then practice diagnosing connectivity symptoms. A quality CompTIA A+ training program should help you connect individual concepts into a troubleshooting process.

How to Use a CompTIA A+ Study Guide

A CompTIA A+ certification study guide works best as a structured reference rather than something you read from beginning to end without testing yourself. After each major topic, close the book and explain the concept from memory. Then answer practice questions and investigate every incorrect response. Your CompTIA A+ study materials should ideally include current exam objectives, technical explanations, hands-on exercises, practice questions, and revision notes. Avoid building your entire preparation around "questions that appeared on the exam." The objective is to understand the subject well enough to solve unfamiliar scenarios.

CompTIA A+ Practice Test Strategy

A CompTIA A+ practice test becomes useful when you analyze your mistakes.Use this cycle:Practice test → Identify weak domain → Study the concept → Repeat questions → Take another timed testDon't judge readiness from one impressive score. Look for consistent performance across different practice sets. A mock CompTIA A+ exam should also be taken under realistic conditions. Avoid checking answers immediately after each question. Complete the test first, record your score, and then review your mistakes.

How Hard Is the CompTIA A+ Exam?

The difficulty of the CompTIA A+ exam depends heavily on your existing experience. Someone who regularly builds computers, troubleshoots operating systems, configures networks, and works with users may find many concepts familiar. A complete beginner will need more time because the certification introduces a wide vocabulary and several technical domains. The challenging part isn't necessarily one exceptionally advanced topic. It is the breadth of knowledge combined with scenario-based troubleshooting. That is why hands-on experience can significantly improve preparation.

How Long Does It Take to Study for CompTIA A+?

There is no universal study period. A beginner studying consistently may need several months, while someone already working in IT support may require considerably less preparation. A practical approach is to study Core 1 first, take practice assessments, and use your results to determine whether you are ready to schedule the exam. Rather than asking only how long to study for CompTIA A+, ask whether you can consistently explain and apply the major objectives without depending on memorized answers.

CompTIA A+ Cost and Exam Voucher

The CompTIA A+ cost depends on the current exam pricing, location, taxes, promotions, training packages, and whether you purchase one exam voucher or a bundle. Because pricing can change, candidates should check the current official CompTIA pricing before budgeting for the certification. Your total CompTIA A+ certification cost can include more than the examination itself. Consider study guides, training, practice tests, equipment for hands-on practice, and potentially a retake if you do not pass an exam. A CompTIA A+ exam voucher can be useful when purchased through an authorized source, but candidates should compare the total package price rather than choosing a voucher based solely on its advertised discount.

Is CompTIA A+ Worth It?

For people entering IT, CompTIA A+ can be worth it because it establishes a broad technical foundation without tying the learner to one technology vendor. Its value is strongest when combined with practical experience. For example, someone pursuing a help desk position can use A+ knowledge alongside a home lab, troubleshooting projects, customer-service experience, and networking fundamentals. The certification should be viewed as a starting point rather than an endpoint. After building foundational knowledge, candidates can progress toward networking, cybersecurity, cloud, Linux, or other technical specialties.

Does CompTIA A+ Expire?

Yes. CompTIA certifications operate under a renewal system, so candidates should check the current certification renewal requirements and validity period rather than assuming the credential remains permanently current. This matters when planning a long-term certification path. Keep track of your certification status and applicable continuing-education or renewal requirements.

How to Get CompTIA A+ Certification

The basic process is straightforward:

  1. Review the current A+ requirements and exam objectives.
  2. Choose a CompTIA A+ course or self-study approach.
  3. Study Core 1 (220-1201).
  4. Use practice exams to measure readiness.
  5. Schedule and pass Core 1.
  6. Prepare for Core 2 (220-1202).
  7. Pass Core 2.
  8. Maintain your certification according to the current renewal requirements.

Candidates should always verify current policies, pricing, exam availability, and testing procedures before booking.

What About CompTIA A+ 1101 vs. 1201?

The comparison between CompTIA A+ 1101 vs. 1201 is mainly relevant to candidates who have found older study resources online.220-1101 and 220-1102 belong to the previous A+ exam series, while 220-1201 and 220-1202 are the newer 1200-series exams.Do not assume an older CompTIA A+ study guide is suitable simply because its title says "A+." Check the exact exam code and publication date. For a candidate preparing now, using resources aligned specifically with the current exam objectives is the safer approach.

Final Takeaway: Build Skills, Then Prove Them

CompTIA A+ Certification makes the most sense when you use it to build a genuine IT foundation rather than treating it as a memorization exercise. Start with the current 220-1201 and 220-1202 objectives, choose study materials that match those objectives, practice troubleshooting, and use mock exams to identify gaps. If you're a beginner, prioritize understanding how systems work. If you're already working in IT, use your real troubleshooting experience to reinforce the exam concepts. The best next step is simple: check the current A+ objectives first, identify your weakest domains, and build your study plan around those gaps rather than around a random collection of practice questions.

12Aug

ceh v 13 Certification is EC-Council’s Certified Ethical Hacker program focused on ethical hacking, vulnerability assessment, penetration-testing techniques, attack detection, defense, and AI-assisted security work.

ceh v 13 Certification is EC-Council’s Certified Ethical Hacker program focused on ethical hacking, vulnerability assessment, penetration-testing techniques, attack detection, defense, and AI-assisted security work. The CEH knowledge exam contains 125 multiple-choice questions with a 4-hour limit. CEH v13 adds AI-driven techniques across the ethical hacking lifecycle. Candidates can also take the optional 6-hour CEH Practical, which contains 20 hands-on challenges, to progress toward the CEH Master credential.

What Is CEH v13?

CEH v13, or Certified Ethical Hacker CEH v13, is EC-Council’s ethical hacking certification program designed to teach professionals how attackers discover and exploit weaknesses—and how security teams identify, validate, and remediate those weaknesses legally.The current EC Council CEH v13 program has evolved beyond memorizing commands and hacking terminology. EC-Council describes a Learn, Certify, Engage, and Compete framework containing 20 modules, 221 hands-on labs, 550 attack techniques, and access to more than 4,000 hacking and security tools.A major distinction of the current program is CEH v13 AI integration. AI-supported tasks appear across areas such as reconnaissance, network scanning, vulnerability analysis, enumeration, system hacking, web security, and cryptography.For professionals searching for a CEH v13 AI certification, it is important to understand the naming: EC-Council's current CEH material increasingly uses the CEH AI branding while its official CEH pages and curriculum continue to reference the v13 generation.

CEH v13 Certification Exam Details

The standard CEH v13 exam is the knowledge-based certification examination. Passing it earns the CEH certification. The separate practical assessment is optional unless your goal is the CEH Master credential.

Exam DetailCEH Knowledge Exam
ProviderEC-Council
FormatMultiple choice
Number of questions125
Duration4 hours
DeliveryECC exam portal / approved testing options
Main focusEthical hacking knowledge and methodology
Passing requirementForm-based cut score
Practical examSeparate and optional for standard CEH
CEH MasterRequires knowledge + practical exams

EC-Council confirms that the knowledge examination covers information-security threats, attack vectors, attack detection, attack prevention, procedures, methodologies, and related ethical hacking competencies.

What Is the CEH v13 Passing Score?

There is not one universal CEH v13 passing score applied to every exam form.EC-Council states that different exam forms contain different question combinations and use calculated cut scores. Its current FAQ says typical passing cut scores range from 65% to 85%. Therefore, claims that every candidate must simply achieve one fixed percentage can be misleading.This also explains why searches for CEH passing score v13 can produce conflicting numbers.

CEH v13 Blueprint and Exam Domains

The official CEH exam blueprint v3.0 referenced in EC-Council's candidate documentation divides the knowledge exam across seven broad areas.

CEH Exam Blueprint DomainWeight
Background21.79%
Analysis / Assessment12.73%
Security23.73%
Tools / Systems / Programs28.91%
Procedures / Methodology8.77%
Regulation / Policy1.90%
Ethics2.17%

The CEH v13 blueprint matters because it shows an important exam-preparation reality: tools, systems, programs, security controls, and technical background represent a large share of assessed knowledge. The CEH blueprint v13 should therefore guide study time rather than treating all topics equally.Candidates looking for CEH v13 objectives, CEH v13 exam blueprint, CEH syllabus v13, or CEH study guide v13 should separate two things: the exam blueprint defines assessed competencies, while the training curriculum provides the broader learning path.

CEH v13 Syllabus and Modules

The official CEH v13 course outline consists of 20 modules.

  1. Introduction to Ethical Hacking
  2. Footprinting and Reconnaissance
  3. Scanning Networks
  4. Enumeration
  5. Vulnerability Analysis
  6. System Hacking
  7. Malware Threats
  8. Sniffing
  9. Social Engineering
  10. Denial-of-Service
  11. Session Hijacking
  12. Evading IDS, Firewalls, and Honeypots
  13. Hacking Web Servers
  14. Hacking Web Applications
  15. SQL Injection
  16. Hacking Wireless Networks
  17. Hacking Mobile Platforms
  18. IoT and OT Hacking
  19. Cloud Computing
  20. Cryptography

The CEH v13 modules move from reconnaissance and discovery into exploitation, web security, wireless environments, mobile platforms, cloud systems, IoT/OT, and cryptography. AI-related activities are embedded throughout several modules rather than being isolated in one short AI chapter.For a useful CEH v13 study guide, organize your preparation around attack workflows rather than memorizing hundreds of disconnected CEH v13 tools. Understand why a technique is used, what evidence it generates, what vulnerability enables it, and which control mitigates it.

CEH v13 Practical Exam

The CEH v13 practical is a separate performance-based examination.Candidates receive 6 hours to complete 20 real-world challenges in a live cyber-range environment involving virtual machines, networks, applications, and security-testing scenarios.Typical CEH v13 practical exam skills include:

  • Network and port scanning
  • Vulnerability identification
  • System attacks
  • Web application assessment
  • SQL injection
  • Session-related attacks
  • Security-tool usage
  • Network and protocol analysis

Passing only the knowledge examination earns CEH. Completing the required knowledge and practical examinations allows candidates to pursue the CEH Master designation.That distinction is important when comparing a standard CEH certification v13 package against programs advertising practical preparation.

CEH v13 Certification Cost and Exam Voucher Prices

The total CEH v13 certification cost depends on whether you purchase only an examination voucher or combine the exam with official CEH v13 training, labs, courseware, or an instructor-led program.As of August 2026, EC-Council's official store lists:

ItemCurrent Listed Price
CEH Exam Voucher – RPSUS$950
CEH Exam Voucher – Pearson VUEUS$1,199
CEH Practical ExamUS$550
CEH Exam PrepUS$149

The RPS voucher covers EC-Council's remotely proctored knowledge exam, while the Pearson VUE option is listed separately. Official vouchers are generally valid for one year from release.Therefore, searches for CEH v13 exam cost, CEH v13 cost, CEH v13 price, or CEH v13 AI certification cost should not assume that training, practical testing, and the knowledge exam are one fixed-price product.

CEH v13 Exam Cost in India

The CEH v13 exam cost in India can vary because training-provider packages, taxes, currency conversion, promotions, and delivery methods may differ. EC-Council also states that CEH training prices vary by region and training format.Always confirm what a quoted price includes before paying.If you plan to buy CEH v13 exam voucher access, check whether the offer includes the knowledge examination only, official training, labs, exam preparation, retakes, or the practical exam.

CEH v13 Eligibility Requirements

There are two primary routes to the CEH examination.Official training route: Candidates completing approved CEH training can become eligible for the certification examination through that route.Experience-based route: Candidates skipping official training must apply for eligibility. EC-Council's candidate guidance specifies two years of information-security-related work experience for the self-study eligibility route.This makes a structured CEH v13 course or CEH v13 online course especially useful for candidates who want guided labs, formal study material, and an integrated certification pathway.

CEH v13 vs v12: What Changed?

The biggest difference in CEH v13 vs v12 is the expanded integration of artificial intelligence into ethical hacking workflows.EC-Council announced v13 as an AI-integrated evolution of CEH, incorporating AI into activities such as reconnaissance, scanning, vulnerability analysis, exploitation-related workflows, and other security tasks.

AreaCEH v12CEH v13
Core ethical hackingYesYes
Reconnaissance and scanningYesYes
Web, cloud and network attacksYesYes
AI-assisted hacking workflowsLimitedMajor focus
AI security conceptsLimitedExpanded
AI-driven automationLimitedIntegrated

So when evaluating CEH v12 vs v13, do not think of v13 as simply a rewritten textbook. Its main strategic change is teaching candidates how AI can assist ethical-hacking activities while maintaining the traditional attack-and-defense foundation.

How to Prepare for the CEH v13 Exam

A strong CEH v13 training plan should combine exam coverage with repeated technical practice.

  1. Start with networking fundamentals. Know TCP/IP, ports, DNS, HTTP/S, routing, operating systems, authentication, and basic security controls.
  2. Map study topics to the CEH v13 exam blueprint. Give higher-weighted areas more revision time.
  3. Build practical familiarity. Practice reconnaissance, Nmap scanning, enumeration, vulnerability assessment, packet analysis, web testing, and Linux/Windows administration only in authorized lab environments.
  4. Study attack and defense together. For every technique, understand detection and mitigation.
  5. Use updated CEH v13 study material. Older material can miss AI-assisted workflows and newer cloud, IoT, mobile, and application-security topics.
  6. Practice timed questions. A 125-question, four-hour exam requires both technical knowledge and efficient decision-making.
  7. Prepare separately for practical testing. A multiple-choice study strategy alone is not enough for the CEH Practical.

Is CEH v13 Worth It?

The CEH v13 certification is most relevant for professionals building skills in ethical hacking, vulnerability assessment, security operations, penetration-testing foundations, security engineering, and cyber defense.Its strongest value comes when the credential is combined with genuine hands-on ability. Knowing what Nmap, Wireshark, vulnerability scanners, exploitation frameworks, web-testing tools, and AI-assisted security utilities do is useful; knowing when, why, and legally where to use them is what turns certification knowledge into professional capability.For candidates asking what is CEH v13 or whether CEH v13 current version material is worth studying, prioritize the current official curriculum, blueprint-aligned preparation, practical lab experience, and AI-enabled workflows. Choose your CEH v13 exam voucher only after deciding whether you need the knowledge exam alone or a broader package containing training and practical preparation.

The ASIS PCI certification, formally the Professional Certified Investigator (PCI®), is an experience-based board certification from ASIS International for professionals who manage investigations, collect and assess evidence, conduct interviews and surveillance, and present investigative findings. Candidates need three to five years of investigations experience depending on education, including at least two years in case management. The exam has 140 multiple-choice questions, lasts 2.5 hours, and tests Professional Responsibility, Investigative Techniques and Procedures, and Case Presentation across real-world security investigation scenarios.

What Is the ASIS PCI certification?

The ASIS PCI certification is the Professional Certified Investigator (PCI®) credential offered by ASIS International. It is designed for experienced investigation professionals whose work involves case management, evidence collection, investigative techniques, reporting, and presentation of findings. Unlike a basic investigation course, the credential does not simply prove that you completed training. ASIS board certification combines documented professional experience with a formal examination.The professional certified investigator PCI credential can be particularly relevant for professionals working in:

  • Corporate investigations
  • Fraud and financial investigations
  • Loss prevention
  • Workplace investigations
  • Forensics
  • High-tech and cybercrime investigations
  • Insurance fraud
  • Threat assessment
  • White-collar crime
  • Property and casualty investigations
  • Security and risk functions

One important distinction: ASIS PCI is not PCI DSS certification. If you search for PCI Security Certification, you may see results relating to payment card security. The ASIS credential discussed here certifies an individual investigator's professional competence, not an organization's payment-card compliance.

Professional Certified Investigator PCI Certification: Who Is It For?

The Professional Certified Investigator PCI Certification is best suited to professionals who already investigate cases rather than people trying to enter investigations with no practical experience. Strong candidate profiles include corporate investigators, internal investigators, fraud specialists, loss-prevention professionals, security investigators, compliance investigators and experienced professionals moving from law enforcement or government investigation roles into corporate security. This is also an important distinction when discussing PCI Certification for Individuals: ASIS certifies the qualified professional. It is not a company-level security certification. PCI validates specialized investigation capabilities, including evaluating cases, selecting case-management strategies and gathering information through techniques such as surveillance, interviews and interrogations.

PCI Certification Requirements

The PCI Certification Requirements depend partly on your level of higher education. Every route requires significant investigations experience and at least two years of case-management experience.

Education LevelInvestigations ExperienceIf You Hold APPCase Management
No higher education degree5 years4 yearsAt least 2 years
Bachelor's degree or equivalent4 years3 yearsAt least 2 years
Master's degree or equivalent3 years3 yearsAt least 2 years

Case management involves coordinating and directing an investigation using suitable resources and investigative disciplines, then evaluating the collected information to determine the facts and findings of the case. Applicants must also have relevant professional security experience and satisfy applicable certification conduct and application requirements. A useful eligibility insight is that performing isolated investigative tasks is not necessarily the same as having case-management experience. If you primarily collect evidence or conduct interviews but another person plans, directs and coordinates the complete investigation, verify carefully whether your experience meets the case-management requirement before applying.

ASIS PCI Certification Exam Format

The ASIS PCI Certification examination focuses heavily on applying investigation knowledge rather than simply memorizing definitions.

Exam DetailPCI Information
Total questions140
Scored questions125
Unscored/pretest questions15
Question formatMultiple choice
Exam time2.5 hours
Passing scaled score650 or higher
Testing providerPrometric
Testing optionsTest center or remote proctored
AvailabilityYear-round
LanguagesEnglish and Spanish

Candidates cannot identify which 15 questions are unscored, so every question should be treated as if it contributes to the final result. The examination uses scaled scoring rather than simply calculating a raw percentage of questions answered correctly.

ASIS PCI Exam Domains

The examination covers three major domains:

DomainExam Weight
Professional Responsibility28%
Investigative Techniques and Procedures52%
Case Presentation20%

The weighting immediately shows where preparation effort should go. Investigative Techniques and Procedures represents 52% of the examination, making practical investigative decision-making the largest part of the test.Professional Responsibility accounts for 28%, while Case Presentation represents 20%.

What Do the Domains Actually Test?

Professional Responsibility addresses ethical issues, applicable laws and regulations, case assessment, investigative strategy, risk, resources and professional decision-making.Investigative Techniques and Procedures is the core of the exam. Candidates should be comfortable applying methods connected with information collection, evidence, interviews, surveillance, investigative technologies, forensic concepts, specialized investigations and related procedures.Case Presentation focuses on turning investigative work into defensible findings. This includes preparing reports that support conclusions and communicating investigative results appropriately.That structure explains why experienced investigators may still find the exam challenging. Knowing how your employer conducts investigations is not enough. Candidates must understand professional investigation principles and apply them in different scenarios.

ASIS PCI Certification Cost

The ASIS PCI certification cost varies according to ASIS membership and applicable market classifications.

Candidate CategoryExam Fee
ASIS Member$580
ASIS Member – Emerging Market 1$480
ASIS Member – Emerging Market 2$460
Nonmember$910
Nonmember – Emerging Market 1$720
Nonmember – Emerging Market 2$680

The standard retake fee may also apply if a candidate needs another attempt.Therefore, when calculating the total ASIS PCI Certification Cost, do not consider only the examination fee. Your overall preparation budget may also include:

  • Official reference materials
  • Study guides
  • Practice questions
  • Mock examinations
  • Review courses
  • PCI Certification Training

ASIS membership is not mandatory for earning the credential, although members may receive reduced certification-related pricing. Because certification pricing can change, candidates should always confirm the latest PCI Certification Cost before submitting an application.

How to Get PCI Certification

The How to Get PCI Certification process involves several important steps.

  1. Confirm your eligibility.
    Match your education and investigation experience to the required eligibility pathway.
  2. Verify your case-management experience.
    Make sure you can document at least two years of qualifying case-management work.
  3. Prepare your application information.
    You may need professional history, education documentation, references, supervisor details and other supporting information.
  4. Submit the certification application.
  5. Receive authorization to test.
  6. Schedule your examination.
    Candidates may be able to choose between a testing center and remote-proctored examination.
  7. Prepare using the current examination Body of Knowledge.
  8. Take and pass the PCI examination.
  9. Maintain the certification through continuing professional education.

The PCI Certification Process is therefore more than simply purchasing an exam voucher and booking a test. Experience verification is an important part of certification. Candidates should describe their investigation responsibilities clearly and accurately when submitting their application.

PCI Certification Training: How to Prepare Effectively

Effective PCI Certification Training should be built around scenarios rather than endless memorization. Candidates should begin by reviewing the current Body of Knowledge and evaluating their experience against each exam domain.A focused preparation plan should include:

  • 52% emphASIS on investigative techniques and procedures
  • Scenario-based investigation questions
  • Ethical and legal issue analysis
  • Interview and interrogation concepts
  • Surveillance principles
  • Evidence and information handling
  • Investigation planning
  • Case-management strategies
  • Report preparation
  • Presentation of investigative findings
  • Timed mock examinations
  • Review of weak domains after practice tests

A common preparation mistake is spending equal study time on every domain.The examination weights are 28%, 52% and 20%, which means candidates should place additional preparation emphasis on Investigative Techniques and Procedures while maintaining adequate knowledge across all three areas. Candidates should also practice answering questions that ask for the BEST, MOST appropriate, FIRST, or PRIMARY investigative action.These questions test judgment rather than simple recall.

ASIS PCI vs Other Security Certifications

People searching ASIS PCI, PCI certification ASIS, or similar phrases sometimes confuse PCI with broader cybersecurity or security-management credentials.PCI has a very specific specialization: professional investigations.It is most relevant when your work involves:

  • Managing investigations
  • Conducting interviews
  • Collecting evidence
  • Evaluating investigative information
  • Managing investigative resources
  • Developing case strategies
  • Preparing investigative reports
  • Presenting findings

If your role primarily involves enterprise security leadership, another management-focused security credential may be more appropriate. If your work is mainly focused on physical-security assessments and protection systems, a physical-security credential may align better. PCI provides the strongest alignment when professional investigations form a significant part of your job responsibilities.

Benefits of ASIS PCI Certification

Earning the ASIS PCI Certification can help experienced professionals demonstrate specialized knowledge in professional investigations.Potential benefits include:

  • Professional credibility in investigation-related roles
  • Formal validation of investigative experience
  • Recognition of case-management skills
  • Stronger professional positioning
  • Greater credibility when handling complex investigations
  • Validation of investigative reporting skills
  • Improved understanding of professional standards
  • Career development opportunities
  • Broader knowledge beyond employer-specific procedures

For experienced investigators, the certification can help demonstrate that their abilities extend beyond one organization, industry or internal investigation methodology.

Is the ASIS PCI Certification Worth It?

The credential can be valuable for experienced investigation professionals who want formal third-party recognition of their expertise. Its value is strongest when the certification matches the work you already perform.For example, a corporate fraud investigator who manages complex investigations can use PCI to validate a broader professional skill set covering:

  • Investigation planning
  • Information gathering
  • Professional responsibility
  • Investigative techniques
  • Case management
  • Evidence handling
  • Reporting
  • Presentation of findings

The certification is less suitable as an entry-level credential because the eligibility requirements are deliberately built around professional experience. Someone with no investigation background should first focus on developing practical investigation knowledge and professional experience before pursuing PCI.

Your Next Step Toward PCI Certification

Start by comparing your education, total investigation experience and two years of case-management experience against the PCI eligibility requirements.Then evaluate your preparation against the examination weighting:

  • Professional Responsibility – 28%
  • Investigative Techniques and Procedures – 52%
  • Case Presentation – 20%

If you already meet the experience requirements, move from general reading to structured, scenario-driven preparation. The ASIS PCI certification is designed to test how effectively you apply investigative judgment, manage cases and communicate findings—not simply how many investigation terms you can memorize.

11Aug

OSP Certification, officially known as the BICSI Outside Plant Designer™ (OSP) credential, validates a professional’s ability to design and integrate outside plant telecommunications infrastructure.


OSP Certification, officially known as the BICSI Outside Plant Designer™ (OSP) credential, validates a professional’s ability to design and integrate outside plant telecommunications infrastructure. It covers aerial, underground, and direct-buried systems, route planning, cabling, pathways, grounding, bonding, project planning, and cost considerations. Candidates can qualify through a current RCDD credential or relevant OSP experience plus documented education. The current exam contains 100 questions, allows 2 hours, and is delivered through Pearson VUE.

What Is OSP Certification?

If you are researching what is osp certification, it is important to distinguish BICSI's credential from general telecommunications training.The BICSI Outside Plant Designer™ credential is intended for ICT professionals who design communications infrastructure located outside buildings. BICSI describes the credential as recognition for people with extensive knowledge and experience in designing new OSP systems and integrating existing infrastructure.Outside plant projects can include infrastructure connecting buildings, campuses, facilities, telecommunications networks, and other locations through:

  • Underground pathways
  • Direct-buried cabling
  • Aerial cable systems
  • Optical fiber infrastructure
  • Copper telecommunications cabling
  • Poles, ducts, conduits, maintenance holes, and pathways
  • Grounding and bonding systems
  • Rights-of-way and route planning
  • Existing infrastructure integration

BICSI identifies its OSP credential as a major industry designation for aerial and direct-burial plant expertise.For experienced designers, the value is not simply knowing how cable is installed. The real skill is making technically defensible design decisions while balancing capacity, physical environment, pathway constraints, standards, expansion requirements, constructability, reliability, and cost.

OSP Certification Exam at a Glance

Here is a simple overview of the current osp certification requirements and examination structure.

OSP Certification DetailCurrent Information
CredentialBICSI Outside Plant Designer™ (OSP)
Certification BodyBICSI
Exam Questions100 questions
Exam Duration2 hours
Delivery MethodComputer-based testing
Testing ProviderPearson VUE
Eligibility Option 1Hold a current RCDD credential
Eligibility Option 22 years of applicable OSP experience + required education
Required Education under Option 2Minimum 32 documented hours
Credential Cycle3 years
Renewal Requirement24 CECs during the three-year cycle

BICSI confirms the 100-question, two-hour examination, while its certification handbook states that OSP credential holders must earn 24 continuing education credits within the three-year credential cycle.

BICSI OSP Designer Certification Requirements

The bicsi osp designer certification requirements are especially important because professional experience is part of the qualification process.BICSI currently provides two main eligibility paths.

Option 1: Current RCDD Credential

You can qualify to apply for the OSP certification examination if you hold a current BICSI RCDD credential.This route makes sense because an RCDD already demonstrates broader ICT infrastructure design knowledge.

Option 2: OSP Experience and Education

Candidates without the qualifying RCDD credential can meet the bicsi osp designer certification eligibility requirements experience pathway through:

  • Two years of verifiable full-time-equivalent experience involving OSP design and/or installation
  • At least 32 hours of documented continuing education in OSP design and/or installation

The education may include qualifying BICSI education and other documented industry training that meets BICSI's requirements.This is an important distinction: OSP is designed for professionals with practical exposure, not candidates relying entirely on memorized textbook concepts.

What Does an OSP Designer Actually Need to Know?

A strong osp design program should go beyond examination terminology and develop the decision-making skills used during actual outside plant projects.An OSP designer may need to evaluate:

Route Selection

A route that appears shortest on a drawing may not be the best engineering choice.Designers need to consider:

  • Existing utilities
  • Physical obstructions
  • Easements and rights-of-way
  • Maintenance accessibility
  • Environmental exposure
  • Future expansion
  • Installation cost
  • Network resilience

Underground Infrastructure

Underground design can involve conduit systems, maintenance holes, handholes, pathway capacity, cable pulling considerations, separation requirements, and future growth.

Direct-Buried Infrastructure

Direct burial removes some pathway infrastructure but introduces different concerns involving soil conditions, cable protection, depth, route marking, environmental risk, and future maintenance.

Aerial Infrastructure

Aerial OSP work can require knowledge of poles, clearances, support structures, guying, loading, attachment locations, cable placement, and environmental conditions.BICSI's official OSP102 Applied Outside Plant Design course specifically covers design techniques for underground, direct-buried, and aerial applications.

What Should OSP Designer Training Cover?

Effective osp designer training should prepare professionals to solve design problems rather than memorize isolated definitions.A useful osp design training plan should include:

  1. OSP infrastructure fundamentals
  2. Site and pre-design assessment
  3. Codes, standards, and regulations
  4. Route selection
  5. Underground pathway design
  6. Direct-buried plant design
  7. Aerial plant design
  8. Cable and media selection
  9. Grounding and bonding
  10. Electrical protection
  11. Rights-of-way
  12. Existing infrastructure assessment
  13. Planning and documentation
  14. Cost estimating
  15. Scenario-based design practice

BICSI's introductory OSP curriculum specifically addresses codes and standards, pre-job assessments, underground pathways, direct-buried pathways, aerial structures, grounding and bonding, electrical protection, and rights-of-way.That gives candidates a useful clue about how to prepare: understand why a design choice is correct, not only what the technical term means.

OSP Training Certification vs OSP Credential

Candidates sometimes treat osp training certification and the OSP credential as interchangeable. They are not.Completing an OSP course can build knowledge and may provide documented education, but the BICSI OSP certification requires meeting eligibility requirements and successfully completing the credentialing examination.BICSI's OSP102 course is recommended for professionals preparing for the credential, but the certification exam is a separate credentialing process.So when comparing an osp certificate from a training provider with the BICSI credential, check exactly what is being awarded.A course completion certificate proves training participation. The BICSI OSP designation represents achievement of BICSI's professional credential requirements.

How to Prepare for BICSI OSP Certification

A disciplined preparation strategy is more effective than reading hundreds of pages without a plan.

1. Start With the Exam Blueprint

Use the official blueprint to identify how BICSI organizes the tested knowledge. BICSI's published OSP exam content outline begins with areas such as pre-design preparation and assigns examination weighting to major areas.

2. Study the OSPDRM

The Outside Plant Design Reference Manual (OSPDRM), 6th Edition is an official BICSI reference for OSP design and examination preparation. BICSI states that the manual, together with OSP education, serves as a detailed study reference for the OSP design exam.

3. Connect Theory to Real Designs

Do not study underground, direct-buried, and aerial systems as isolated chapters.For each scenario, ask:

  • Which route is technically practical?
  • Which pathway protects the infrastructure?
  • What environmental risks exist?
  • What standards or regulations affect the design?
  • How will maintenance crews access the plant?
  • What capacity will future expansion require?
  • What design creates unnecessary cost?

This type of reasoning is much closer to professional design work.

4. Use Scenario-Based Practice Questions

Practice should test judgment.A good question should force you to compare several technically plausible choices and determine the best design decision based on project conditions.

5. Review Weak Areas Separately

Do not repeatedly study topics you already understand.Track mistakes by category, such as:

  • Route planning
  • Aerial systems
  • Underground systems
  • Direct burial
  • Cable selection
  • Grounding and bonding
  • Protection
  • Documentation
  • Estimating

Then build targeted revision sessions.

OSP Certification Cost

BICSI's current published OSP certification handbook lists the examination application fee at $510 for BICSI members and $725 for nonmembers, including the first Pearson VUE exam attempt. Published retest pricing is $230 for members and $355 for nonmembers.BICSI's online store also currently lists the standard OSP exam fee at $725, consistent with the nonmember price.Training, manuals, membership, and other preparation resources can add separate costs.Because pricing can change, candidates should verify current BICSI fees before registering.

BICSI OSP Certification and RCDD: How Are They Related?

The terms rcdd osp certification and bicsi rcdd/osp certification are sometimes searched together, but these are separate professional credentials.RCDD focuses broadly on ICT infrastructure design, while OSP concentrates more deeply on outside plant systems.There is still a strong connection between them: holding a current RCDD is one of BICSI's accepted eligibility routes for the OSP examination.The relationship also works strategically in the other direction. BICSI currently recognizes an OSP credential as one qualification that can contribute to certain RCDD eligibility pathways when combined with required ICT design experience.For professionals responsible for both building distribution and campus or external infrastructure, holding both credentials can demonstrate a broader design capability.

Is OSP Design Certification Worth Pursuing?

An osp design certification is most relevant when your work involves telecommunications pathways beyond the building entrance.It can be especially useful for:

  • Outside plant designers
  • Telecommunications engineers
  • ICT consultants
  • Network infrastructure designers
  • Fiber infrastructure professionals
  • Utility communications specialists
  • Campus network designers
  • RCDDs expanding into OSP
  • Project professionals working with external ICT infrastructure

BICSI notes that many organizations require the OSP credential for design or installation personnel working on outside plant projects.The strongest reason to pursue it, however, is specialization. Designing an OSP system requires decisions that can affect construction cost, network reliability, maintenance effort, expansion capability, and infrastructure life cycle.A poorly selected pathway can remain an operational problem for decades. A well-designed route can support multiple technology generations.

OSP Certifications: What Makes BICSI Different?

There may be multiple training-based osp certifications in the market, but the BICSI credential is built around documented professional eligibility, formal examination, and continuing professional development.Credential holders must maintain the designation rather than treating certification as a one-time achievement. BICSI states that the OSP credential remains valid for a three-year cycle and requires 24 CECs for renewal.That continuing-education requirement matters in a field affected by evolving fiber technologies, construction methods, standards, materials, deployment practices, and network capacity requirements.

Your Next Step Toward OSP Certification

Treat OSP Certification as a professional design credential, not simply another exam.First confirm that you meet BICSI's eligibility requirements. Then use the official exam blueprint and OSPDRM, strengthen your understanding of underground, aerial, and direct-buried infrastructure, and practice applying those concepts to realistic design scenarios.For candidates who need a structured learning path, a focused osp designer training program can help organize the technical material, identify weak design areas, and turn OSP theory into exam-ready problem-solving skills.

OSP certifications usually refers to the BICSI Outside Plant Designer™ (OSP) credential, which validates a professional’s ability to design outside plant ICT infrastructure. It covers route planning, underground, direct-buried and aerial pathways, media selection, grounding and bonding, rights-of-way, estimating, and project coordination. Candidates qualify through a current RCDD credential or documented OSP experience plus continuing education. The current exam has 100 questions, allows two hours, and is delivered through Pearson VUE. Certification must then be maintained through BICSI recertification requirements.

What Are OSP Certifications?

For professionals asking what is OSP certification, OSP stands for Outside Plant, referring to telecommunications and ICT infrastructure installed outside buildings and extending between facilities, campuses, utility routes, streets, and other external environments.TheBICSI OSP certification is specifically the BICSI Outside Plant Designer™ (OSP) credential. BICSI describes it as a leading designation focused on aerial and direct-burial outside plant work. An OSP designer may work with:

  • Fiber-optic and copper cable routes
  • Underground duct and conduit systems
  • Handholes, maintenance holes, and pull points
  • Direct-buried communications infrastructure
  • Aerial cable routes and support structures
  • Campus telecommunications systems
  • Grounding, bonding, and electrical protection
  • Rights-of-way and route restrictions
  • Cost estimates and project planning

The important distinction is that OSP work is not simply about selecting cable. A competent designer must consider route viability, physical protection, capacity, maintainability, environmental conditions, codes, constructability, cost, and future expansion as parts of one design.

Why OSP Certifications Matter for ICT Professionals

A strong OSP design certification demonstrates expertise in an area that sits between telecommunications engineering, infrastructure design, construction, utility coordination, and project management. BICSI states that many organizations require the OSP credential for personnel involved in outside plant design and installation projects. The credential can be particularly relevant for:

  • Outside plant designers
  • Telecommunications engineers
  • Fiber infrastructure designers
  • ICT consultants
  • Utility telecommunications professionals
  • Network infrastructure engineers
  • Campus infrastructure designers
  • Project managers working on OSP deployments
  • RCDDs expanding into outside plant specialization

The real value comes from being able to make defensible design decisions. Employers and clients need more than someone who knows what a conduit, splice closure, or fiber cable is. They need someone who can determine where infrastructure should run, how it should be protected, what installation method fits the environment, and what the project is likely to cost.

BICSI OSP Designer Certification Requirements

The current BICSI OSP designer certification requirements provide two eligibility routes.

Eligibility PathCurrent Requirement
Option 1Hold a current RCDD® credential
Option 2Have 2 years of verifiable full-time equivalent experience in OSP design and/or installation, plus at least 32 hours of documented continuing education in OSP-related subjects

BICSI publishes these eligibility routes on its official OSP certification information. People searching for BICSI OSP designer certification eligibility requirements experience should pay particular attention to the word verifiable. Practical experience should be documented accurately rather than treated as a general statement that you have worked in networking. OSP experience can involve design or installation activities associated with real outside plant infrastructure.

Experience matters more than job title

A job title such as Network Engineer or Telecom Engineer does not automatically prove OSP design capability.When preparing an application, identify work where you actually participated in areas such as:

  • Route surveys
  • Pathway selection
  • Fiber or copper route planning
  • Aerial or underground infrastructure
  • Construction documentation
  • Cable calculations
  • Cost estimates
  • Rights-of-way
  • Installation coordination

This makes your experience easier to explain and document.

BICSI OSP Exam Format

The BICSI OSP designer certification requires candidates to pass a computer-based examination.

Exam DetailCurrent Information
Questions100
Exam Time2 hours
DeliveryPearson VUE computer-based testing
Member Application Fee$510
Nonmember Application Fee$725
First AttemptIncluded with application fee

BICSI currently lists these exam details and fees on its OSP credential information. Fees can change, so candidates should confirm pricing with BICSI before submitting an application.

What makes the exam challenging?

The difficulty is not simply memorizing definitions. OSP designers regularly face situations where several solutions are technically possible, but only one makes the most sense after considering route limitations, cable type, installation method, safety, regulations, cost, maintenance, and future capacity. That is why strong preparation should focus on design judgment rather than isolated facts.

What Should OSP Designer Training Cover?

Effective OSP designer training should reflect the decisions made during real outside plant projects. BICSI's official OSP102 Applied Outside Plant Design course covers campus OSP projects and design techniques involving underground, direct-buried, and aerial cable plant applications. It also uses design scenarios involving route design, media selection, planning, and cost estimation. A serious OSP design training plan should therefore cover:

  1. Outside Plant Fundamentals
    Understand OSP infrastructure components and how systems connect facilities.
  2. Route Planning
    Evaluate possible routes based on physical conditions, accessibility, risk, cost, and future requirements.
  3. Underground Infrastructure
    Understand pathways, spaces, conduit systems, pulling considerations, and access points.
  4. Direct-Buried Infrastructure
    Learn where direct burial may be appropriate and what protection and planning issues affect the design.
  5. Aerial Plant Design
    Understand support structures, clearances, pathways, and deployment considerations.
  6. Media Selection
    Select appropriate telecommunications media based on distance, capacity, environment, and application requirements.
  7. Grounding and Bonding
    Apply appropriate grounding, bonding, and electrical protection principles.
  8. Cost Estimation
    Translate the technical design into materials, labor considerations, and realistic project costs.
  9. Codes and Rights-of-Way
    Understand the effect of regulations, standards, public property, private property, and route permissions.

These subjects are also reflected in BICSI's OSP education materials.

OSP Design Program vs Certification

An OSP design program teaches knowledge and design methods. The professional credential verifies that a candidate has satisfied BICSI's eligibility requirements and passed the certification examination. That distinction matters. Completing a course does not automatically make someone OSP-certified. Similarly, an OSP training certification offered by a training provider should not be confused with the official BICSI OSP credential unless the provider is specifically describing the BICSI certification pathway. BICSI's OSP102 course is recommended for professionals preparing for the OSP credential, but the exam application is a separate process.

OSP102 Applied Outside Plant Design

BICSI's official OSP102 course is one of the most directly aligned OSP design program options for professionals preparing for this field.The current course provides 35 continuing education credits (CECs) and covers areas including:

  • OSP infrastructure components
  • Pathways and spaces
  • Route design
  • Planning
  • Grounding and bonding
  • Underground systems
  • Direct-buried systems
  • Aerial routes
  • Cost estimation

BICSI states that the course is intended for OSP professionals and for BICSI TECH, RTPM, and RCDD credential holders who want to advance into Outside Plant design. An effective independent OSP design training plan should mirror these practical design areas even when a candidate chooses a different preparation route.

OSP Certification vs RCDD

The terms RCDD OSP certification and BICSI RCDD/OSP certification sometimes appear together, but they represent different BICSI credentials.

OSPRCDD
Specialized in Outside Plant designBroader ICT and telecommunications distribution design credential
Strong emphasis on aerial, underground, and direct-buried infrastructureCovers broader telecommunications distribution systems
Current RCDD holders can qualify for OSP through eligibility Option 1Current OSP holders can help satisfy one RCDD eligibility path when combined with required ICT design experience
Best suited to dedicated OSP workBest suited to broader ICT design responsibility

BICSI describes the RCDD as a credential demonstrating mastery of ICT and telecommunications distribution system design. The credentials therefore complement each other rather than serving as simple replacements. BICSI also lists a current OSP credential among the certifications that can contribute to one RCDD eligibility route when the required design experience is also met.

How to Earn the OSP Certificate

The path to an OSP certificate can be organized into a straightforward process:

  1. Check your eligibility.
  2. Document relevant OSP experience.
  3. Complete required education if using the experience-based route.
  4. Review current BICSI OSP resources.
  5. Build a structured study plan.
  6. Practice scenario-based design decisions.
  7. Submit the OSP exam application and résumé.
  8. Schedule the exam through Pearson VUE after approval.
  9. Pass the certification exam.
  10. Maintain the credential through continuing education.

BICSI requires an online OSP exam application and current résumé as part of the application process.

Maintaining Your OSP Certification

Earning the credential is not the end of the process. BICSI requires OSP credential holders to earn 24 continuing education credits within a three-year certification cycle for recertification. This requirement matters because outside plant design continues to change as fiber deployment methods, standards, construction practices, materials, and project requirements evolve. Professionals should avoid waiting until the final months of the cycle to think about renewal. Track approved CEC activity throughout the three-year period and maintain documentation.

How to Prepare More Effectively

Candidates often make one mistake: studying OSP as a collection of individual components. A stronger approach is to think like a designer.For every topic, ask:

  • What problem is the design solving?
  • What environmental conditions affect the route?
  • Which pathway method is appropriate?
  • What happens if capacity increases later?
  • How will technicians access the infrastructure?
  • What safety or regulatory restrictions apply?
  • How does the design affect construction cost?

That approach turns memorized knowledge into applied design reasoning. The official Outside Plant Design Reference Manual (OSPDRM), 6th Edition is also part of BICSI's current OSP educational resources.

Your Next Step Toward OSP Certifications

Before investing heavily in preparation, confirm which eligibility route applies to you. Current RCDD holders have a direct eligibility path, while experienced OSP professionals should document their two years of relevant experience and the required 32 hours of continuing education. Then build your preparation around actual OSP design decisions—not only terminology. Focus on route planning, aerial and underground infrastructure, direct burial, media selection, grounding and bonding, rights-of-way, planning, and cost estimation. That is the difference between preparing merely to answer exam questions and developing the design judgment that makes OSP certifications valuable in real ICT infrastructure projects.


10Aug

The cia Certification is the Certified Internal Auditor® credential issued by The Institute of Internal Auditors (The IIA).

The cia Certification is the Certified Internal Auditor® credential issued by The Institute of Internal Auditors (The IIA). It validates professional capability in internal audit fundamentals, engagement work, and audit-function management. The traditional pathway requires three exams, approved education or an active IAP route, and relevant experience based on education level. Candidates generally have three years to complete program requirements. Current U.S./select-market fees total $990 for members or $1,515 for non-members, before applicable taxes or membership dues, as of 2026.

What Is cia Certification?

The cia certification is the professional credential for becoming a Certified Internal Auditor. It is awarded by the Institute of Internal Auditors, commonly known as The IIA, and focuses specifically on the knowledge and judgment required to perform and manage internal audit work.The IIA describes the CIA as the only globally recognized internal audit certification and reports more than 220,000 CIA professionals across 170 countries.A certified internal auditor certification is particularly relevant for professionals working in:

  • Internal auditing

  • Governance and internal control

  • Enterprise risk management

  • Compliance

  • External audit

  • Quality assurance

  • Audit and assessment functions

One important distinction is that CIA is not simply an accounting credential. Modern cia internal audit work requires professionals to understand risk, governance, controls, evidence, stakeholder expectations, audit planning, engagement execution, and communication.

cia Certification Exam: Current 2026 Structure

The traditional cia certification exam consists of three separate multiple-choice examinations. Candidates do not have to take the parts in numerical order.

CIA Exam PartCurrent FocusQuestionsTimeMember FeeNon-Member Fee
Part 1Internal Audit Fundamentals125150 minutes$310$445
Part 2Internal Audit Engagement100120 minutes$280$415
Part 3Internal Audit Function100120 minutes$280$415

The traditional pathway therefore contains 325 questions across 390 minutes of testing. The IIA identifies the three current content areas as Internal Audit Fundamentals, Internal Audit Engagement, and Internal Audit Function.For anyone researching the certified internal auditor exam, this three-part structure matters because each part demands a different preparation strategy.

Part 1: Internal Audit Fundamentals

Part 1 establishes the professional foundation. Candidates need to understand how internal auditing operates within an organization, including governance, independence, professional standards, risk, controls, and the responsibilities of the internal audit function.

Part 2: Internal Audit Engagement

Part 2 moves closer to actual engagement execution. Preparation should emphasize how auditors plan engagements, collect and evaluate information, document work, exercise professional judgment, and develop supportable findings.

Part 3: Internal Audit Function

Part 3 looks more broadly at managing and delivering an effective internal audit function, including audit planning, operations, quality, engagement results, stakeholder communication, and monitoring.The current CIA syllabus is aligned with modern internal audit practice and The IIA provides official syllabi for all three parts.

cia Certification Requirements and Eligibility

Understanding cia certification requirements before purchasing an exam is essential because passing the tests alone does not automatically satisfy every certification requirement.The current cia certification eligibility structure is largely determined by education and relevant professional experience.

Entry BackgroundExperience Requirement
Master’s degree or equivalent/higher1 year
Bachelor’s degree or equivalent2 years
Active IAP without qualifying degree5 years*

*For the active IAP pathway without a qualifying degree, two of the five required years must be within the previous three years. Degree holders using the IAP route follow the applicable education-based experience requirement.Relevant experience can come from internal audit, quality assurance, risk management, audit/assessment disciplines, compliance, external audit, or internal control.These are the core certified internal auditor requirements candidates should evaluate before applying.For candidates specifically researching certified internal auditor certification requirements, another useful rule is that professional experience does not necessarily have to be completed before sitting for the exams. Candidates with qualifying education can take the examinations before satisfying their full experience requirement, but all program requirements must be completed within the applicable program period.

What if You Do Not Have a Degree?

The current pathway is more flexible than many candidates assume.Students and professionals without a qualifying degree can begin through the Internal Audit Practitioner (IAP) route. The IAP uses CIA Part 1, and an active IAP holder who later enters the CIA program can receive a waiver for Part 1.That makes the answer to questions about requirements for cia certification dependent on your academic and professional background rather than a single universal requirement.

cia Certification Cost in 2026

The published cia certification cost varies according to IIA membership status and location.Current pricing published by The IIA is:

FeeIIA MemberNon-Member
CIA Application$120$240
Part 1$310$445
Part 2$280$415
Part 3$280$415
Total$990$1,515

Therefore, the basic cost of cia certification under the traditional three-exam pathway is $990 at member rates or $1,515 at non-member rates based on current listed pricing.The difference is significant: member pricing reduces the listed application-and-exam total by $525. However, candidates should also consider their applicable membership dues before deciding which route is financially better.If you are specifically comparing cia exam cost, remember that the application fee is separate from the registration fee for each examination.Similarly, searches for certified internal auditor certification cost, certified internal auditor cost, or certified internal auditor exam cost should distinguish between the price of one exam and the complete certification process.The IIA notes that these prices apply in the United States, Canada, and select markets. Local National Institutes may use different pricing, and applicable taxes can also change the final amount.

How to Get the iia CIA Certification

The application process for an iia cia certification is handled through The IIA's Certification Candidate Management System, or CCMS.The practical process is:

  1. Confirm your eligibility pathway.

  2. Gather required education documentation and government-issued identification.

  3. Create or access your CCMS account.

  4. Submit your CIA application and pay the application fee.

  5. Wait for document and application approval.

  6. Register for each required cia exam.

  7. Schedule and complete the examinations.

  8. Submit or complete your experience verification.

  9. Receive the CIA designation after all requirements are satisfied.

Candidates accepted into the traditional program must pass all three exam parts and complete the program requirements within three years.

How Should You Approach cia Exam Preparation?

Effective cia exam preparation should focus less on memorizing isolated definitions and more on applying internal audit principles to realistic decisions.A strong study sequence is:

  • Learn the current syllabus before selecting study materials.

  • Build conceptual understanding before intensive question practice.

  • Study one exam part as a separate project.

  • Practice scenario-based questions regularly.

  • Review why incorrect answers are wrong.

  • Track weak topics instead of repeatedly studying strong areas.

  • Run timed practice sessions before scheduling the examination.

The IIA provides current syllabi, sample questions, and practice resources, including practice questions based on retired examination items. Study materials are not automatically included with standard CIA application or exam registration fees.A structured certified internal auditor exam preparation plan should therefore combine syllabus coverage, question practice, review, and exam-time management.

cia Certification Training: Self-Study or Instructor-Led?

The right cia certification training format depends on your audit experience.Experienced auditors may be comfortable with a self-directed cia certification course, while professionals moving from accounting, finance, compliance, IT audit, or risk management may benefit from instructor guidance that connects exam concepts with internal audit scenarios.When assessing a certified internal auditor course, look for:

  • Alignment with the current CIA syllabus

  • Part-specific lessons

  • Scenario-based practice questions

  • Detailed answer explanations

  • Mock examinations

  • Performance analytics

  • Weak-area revision

  • Access to updated materials

A certified internal auditor online course can be particularly useful for working professionals because preparation can be scheduled around professional responsibilities.However, the phrase cia certification online should not automatically be interpreted as “take every CIA exam from home.” The IIA directs candidates to its testing and Pearson VUE resources for current exam-delivery procedures, so candidates should verify available testing options when scheduling.

Who Should Pursue the CIA?

The credential has strong relevance beyond professionals whose job title literally says “internal auditor.”A cia certified internal auditor pathway can make sense for:

  • Internal auditors seeking progression toward senior or management roles

  • External auditors moving into corporate assurance

  • Risk and compliance professionals

  • Internal-control specialists

  • Finance professionals moving into assurance

  • IT auditors expanding into broader enterprise audit work

  • Audit managers preparing for leadership responsibilities

The value of an iia certified internal auditor is the breadth of professional judgment the credential develops. The exams connect governance, risk, control, engagement execution, audit-function management, quality, and communication rather than testing one narrow technical discipline.That makes this institute of internal auditors certification useful for professionals who want their knowledge to extend from performing individual audit procedures to understanding how the entire internal audit function supports an organization.

Is the CIA Worth Pursuing?

For someone planning a long-term career in internal audit, risk, governance, assurance, or controls, CIA is one of the most directly aligned professional credentials available. The IIA positions it as its globally recognized internal audit designation, with holders operating across 170 countries.The bigger benefit is not simply adding three letters after your name. Proper preparation forces candidates to understand why an audit procedure is appropriate, how evidence supports conclusions, where internal audit independence can be compromised, and how findings should influence organizational action.That distinction matters in senior audit roles, where professional judgment is usually more valuable than mechanical knowledge.

Maintaining Your Certified Internal Auditor Credential

Earning the designation is not the final administrative requirement. Active practicing CIA holders must complete 40 CPE hours annually and renew their certification each year. The IIA's annual renewal period runs from October 1 through December 31.Maintaining your credential therefore requires an ongoing professional-development plan rather than treating the certification as a one-time examination achievement.

Your Next Step: Build a Part-by-Part CIA Plan

Start by checking your certified internal auditor eligibility, calculating your complete expected fees, and downloading the current official syllabus before buying training materials.Then treat each exam part as a separate objective: understand the syllabus, build your knowledge base, practice application-oriented questions, measure weak areas, and schedule the examination only when your performance is consistent.The strongest preparation strategy is not studying the greatest number of hours. It is knowing exactly what the CIA exam expects you to decide as an internal auditor—and being able to make that decision under exam pressure.


The psp certification is the Physical Security Professional (PSP®) board certification from ASIS International for experienced physical security practitioners. It validates competence in security assessment, system design and integration, and implementation of physical security measures. The current exam contains 125 scored questions plus 15 unscored pretest questions, allows 2.5 hours, and covers three domains. Candidates generally need three to five years of relevant experience, depending on education and whether they already hold the APP credential.

What Is PSP Certification?

If you are asking what psp certification is, it is a specialized board certification for professionals who assess physical-security risk, select and design protection systems, and manage the implementation of security measures.The official physical security professional (psp) credential is administered by ASIS International. It is designed for practitioners whose responsibilities go beyond guarding a facility. PSP candidates are expected to understand risk assessment, system requirements, access control, video surveillance, intrusion detection, protective design, procurement, installation, commissioning, and security-program evaluation.For anyone researching psp meaning in security, psp meaning security, psp security meaning, or what is psp in security, PSP stands for Physical Security Professional in the ASIS certification context.A related search such as psp course full form can be misleading because PSP is not the name of a training course. It is the professional certification designation itself.The psp designation is therefore different from a simple attendance-based psp certificate. Candidates must satisfy eligibility requirements and pass a formal certification examination before using the credential. ASIS describes its board certifications as evidence of demonstrated professional knowledge and competency.

ASIS PSP Certification Overview for 2026

The following asis psp certification overview captures the major details candidates should know before applying.

PSP DetailCurrent Information
Certification bodyASIS International
Full namePhysical Security Professional (PSP®)
Exam formatMultiple choice
Total questions140
Scored questions125
Unscored pretest questions15
Exam time2.5 hours
Exam domains3
Experience requirementApproximately 3–5 years, depending on education/APP status
Member exam fee$580
Nonmember exam fee$910
Testing optionsPrometric testing center or remote proctoring
Recertification cycleEvery 3 years
CPE requirement60 CPE hours per cycle

ASIS confirms that the asis psp exam has four answer choices per question, with one correct response. Both unanswered and incorrectly answered questions count against the candidate's result.This makes psp testing less about recognizing isolated definitions and more about selecting the most defensible security decision under realistic constraints.

PSP Certification Requirements: Who Is Eligible?

The psp certification requirements are based primarily on physical-security experience and education.ASIS currently specifies the following pathways.

Without a Higher-Education Degree

Candidates need:

  • Five years of physical security experience, or
  • Four years if they already hold the ASIS APP certification.

With a Master's Degree

Candidates need:

  • A master's degree or international equivalent from an accredited institution, and
  • Three years of physical security experience.

With a Bachelor's Degree

Candidates need:

  • A bachelor's degree or international equivalent from an accredited institution, and
  • Four years of physical security experience, or
  • Three years if they already hold APP.

These are the core asis psp certification requirements and psp requirements, but eligibility does not stop with years of experience.Applicants must also be working full time in a security-related position, meet ASIS's professional-conduct requirements, and agree to follow certification policies and the ASIS Certification Code of Conduct. In practical terms, the psp qualification is aimed at established practitioners rather than complete beginners.

How to Get PSP Certification

Candidates wondering how to get psp certification can think of the process as five stages.

  1. Confirm eligibility. Match your education and physical-security experience against the official requirements.
  2. Document your experience. Prepare a résumé or CV showing work that aligns with the PSP domains.
  3. Prepare your application. ASIS requests applicable educational documentation, three professional references, supervisor information, and payment.
  4. Prepare for the exam. Study the official Body of Knowledge and practice applying physical-security principles to scenarios.
  5. Schedule and take the exam. Approved candidates can test through Prometric according to ASIS scheduling options.

Your résumé deserves particular attention. A generic security job description does not communicate expertise as effectively as experience tied to assessments, system design, integration, procurement, implementation, commissioning, or security-program management.

PSP Exam Domains and Coverage

Understanding psp coverage should drive your study strategy.The current examination covers three weighted domains.

DomainExam WeightWhat You Need to Understand
Physical Security Assessment34%Assets, threats, hazards, vulnerabilities, risk analysis and countermeasures
Application, Design, and Integration of Physical Security Systems35%Requirements, protective measures, electronic systems, CPTED, system design and integration
Implementation of Physical Security Measures31%Bidding, procurement, installation, commissioning, personnel and lifecycle evaluation

Domain 1: Physical Security Assessment – 34%

The first domain tests whether you can build and execute a defensible assessment.Expect concepts involving:

  • Critical asset identification
  • Qualitative and quantitative assessment
  • Threat and hazard evaluation
  • Vulnerability assessment
  • Building plans and environmental conditions
  • Risk-analysis methods
  • Countermeasure selection
  • Cost-benefit analysis
  • Legal and regulatory considerations

A strong physical security professional psp candidate should be able to connect assets, threats and vulnerabilities rather than evaluating each in isolation.

Domain 2: Application, Design, and Integration – 35%

This is the largest domain.It covers design constraints, performance requirements, risk-informed system design and the selection of appropriate countermeasures.Candidates may encounter concepts involving:

  • Barriers and structural protection
  • CPTED
  • Access control
  • Video surveillance
  • Intrusion detection
  • Emergency communication
  • Monitoring systems
  • Power and backup power
  • Network infrastructure
  • Signal transmission
  • Security personnel
  • Project documentation
  • System integration

The key distinction is between knowing what a security technology does and determining whether it meets a defined operational requirement.

Domain 3: Implementation of Physical Security Measures – 31%

The third domain moves from design into delivery.It includes:

  • Pre-bid processes
  • RFP, RFQ and related procurement approaches
  • Vendor evaluation
  • Project management
  • Installation and inspection
  • System integration
  • Commissioning
  • Acceptance testing
  • End-user training
  • Security personnel requirements
  • Preventive and corrective maintenance
  • System lifecycle evaluation

This domain explains why the credential is relevant to consultants, security-system managers and practitioners responsible for real-world implementation—not just policy development.

PSP Exam Format and Testing Experience

The current psp exam contains:

  • 125 scored questions
  • 15 unscored pretest questions
  • 140 total questions
  • Four options per question
  • 2.5 hours of testing time

Candidates researching psp exams, psp test, or asis psp exam questions should understand an important point: ASIS describes its examinations as experience-based.That means memorizing definitions alone is unlikely to produce reliable performance. Candidates often need to determine the best, most appropriate, or operationally defensible response in a scenario.ASIS uses scaled scoring rather than simply publishing a universal raw-percentage pass mark.

PSP Certification Cost and ASIS PSP Exam Cost 2026

The official psp certification cost varies by membership and eligible emerging-market classification.As of the current 2026 ASIS fee page, standard fees are:

Candidate CategoryCurrent Exam Fee
ASIS Member$580
Member – Emerging Market 1$480
Member – Emerging Market 2$460
Nonmember$910
Nonmember – Emerging Market 1$720
Nonmember – Emerging Market 2$680

Therefore, candidates searching asis psp certification cost, asis psp certification cost 2026, psp exam fees, or asis psp exam cost 2026 should use the ASIS fee page rather than older third-party articles.The standard retest fee for CPP, PCI and PSP is currently $480; eligible emerging-market retest rates are lower. Candidates may attempt the examination up to three times during their one-year eligibility period, with at least 60 days between testing dates.Study guides, reference books and other preparation resources are separate expenses.

How to Approach PSP Exam Preparation

Effective psp exam preparation should begin with the Body of Knowledge rather than random question banks.A sensible preparation sequence is:

1. Map Your Experience Against the Domains

Identify which domain resembles your daily work.A security consultant may already be strong in assessment but weaker in procurement. A system integrator may understand cameras and access control but need more work on quantitative risk analysis.

2. Study the Official References

ASIS identifies Protection of Assets: Physical Security, Implementing Physical Protection Systems: A Practical Guide, the Physical Asset Protection Standard, and the Business Continuity Guideline among its PSP reference materials. A structured psp course, asis psp course, or professional psp training can help organize these concepts, but the training should follow the official Body of Knowledge rather than attempt to replace it.

3. Practice Decision-Making

Good training psp exercises should ask questions such as:

  • What should be assessed first?
  • Which control addresses the identified risk?
  • What requirement should exist before choosing technology?
  • Which acceptance test proves the system meets specifications?
  • Which option provides the strongest cost-benefit relationship?

That approach is more valuable than memorizing hundreds of disconnected facts.

4. Use Legitimate Practice Material

ASIS provides a PSP practice exam containing retired exam items and also offers a commercial asis psp practice test. Searches for asis-psp questions or asis-psp exam questions should therefore prioritize legitimate practice material. Avoid asis-psp dumps or purported live exam questions. Besides creating exam-integrity concerns, memorized dumps are a poor substitute for the professional judgment the examination is designed to measure.

What Does Being PSP Certified Actually Demonstrate?

A psp certified professional has demonstrated knowledge across the lifecycle of physical protection: assessing risk, defining requirements, designing systems, integrating controls and overseeing implementation.This makes the psp security certification particularly relevant to professionals working in roles such as:

  • Physical Security Manager
  • Security Consultant
  • Security Systems Manager
  • Corporate Security Specialist
  • Security Project Manager
  • Critical Infrastructure Security Professional
  • Security Design Consultant
  • Security Risk Specialist

The psp credential can also give employers a clearer indication that someone's knowledge extends beyond a single product, technology or facility.For this reason, psp certification security is best viewed as professional validation of applied physical-security expertise rather than vendor-specific technical certification.

PSP vs CPP: Which ASIS Certification Fits Your Career?

People searching for cpp psp certification often assume PSP and CPP represent different experience levels on the same track. The distinction is more about scope.PSP specializes in physical-security assessment, system design/integration, and implementation. CPP addresses broader security management and is intended for more senior security managers; ASIS currently lists five to seven years of related experience plus responsible-charge requirements for CPP. Choose psp asis when your expertise is centered on the physical protection environment. Consider CPP when your responsibilities span enterprise-level security management.That distinction is also useful when researching psp asis certification, psp certification asis, physical security professional psp certification, asis physical security professional (psp), or physical security professional" psp certification asis.

PSP Recertification: Keeping the Credential Active

psp recertification is required every three years.ASIS currently requires certificants to earn 60 Continuing Professional Education hours during each three-year certification cycle. Qualifying activities can include education, instruction, authorship, volunteering, professional service and other approved accomplishments. Current standard recertification application fees are:

  • ASIS members: $180
  • Nonmembers: $220

Emerging-market pricing is also available. This continuing-education requirement is significant: earning the psp cert is not intended to be a one-time test of knowledge. The credential requires professionals to keep developing after certification.

Is the PSP Worth Pursuing?

The asis psp makes the most sense when your work already involves physical-security risk, facilities, protective technology, security design, integration or implementation.It is less suitable for someone with no professional security background because the certification deliberately assumes relevant field experience.ASIS positions the credential as validation of expertise, global professional recognition and a way to strengthen marketplace credibility. The strongest reason to pursue psp security is therefore not simply to add letters after your name. It is to formally demonstrate that you can move from identifying a security problem to designing, selecting, implementing and evaluating an appropriate protection solution.

Your Next Step Toward the Physical Security Professional PSP

Before purchasing a psp course or starting an aggressive study schedule, check your eligibility against ASIS's current requirements and download the official PSP Body of Knowledge.Then assess yourself against all three domains. Build your study plan around the gaps between your current professional experience and the exam blueprint—not around the number of practice questions you can memorize.For an experienced practitioner, the physical security professional psp credential is most valuable when preparation strengthens the same judgment required on real projects: identify the risk correctly, define the requirement clearly, select defensible controls, and verify that the final security solution actually performs as intended.

I BUILT MY SITE FOR FREE USING